Master Key Protection with a Thales Luna HSM
This guide describes the integration of Fudo Enterprise with Thales Luna HSMs, both Luna Cloud HSM and Luna Network HSM.
Fudo Enterprise can use a Hardware Security Module (HSM) to provide hardware-backed protection for its master key. When HSM integration is enabled, Fudo Enterprise communicates with the HSM through the PKCS#11 interface and uses a Key Encryption Key (KEK) protected by the HSM to secure the Fudo Enterprise master key.
HSM integration is optional. By default, Fudo Enterprise uses its standard software-based key protection mechanism.
Note
Fudo Enterprise supports network-accessible HSM providers that provide a Linux x86-64 PKCS#11 client.
How Fudo Enterprise Protects the Master Key
Enabling HSM integration does not replace the Fudo Enterprise master key with an HSM-generated key. Fudo Enterprise continues to use its own master key, which is protected using key wrapping.
A Key Encryption Key (KEK) is protected by the HSM and is non-exportable. The Fudo Enterprise master key is stored in a wrapped form, encrypted using the HSM-protected KEK.
When Fudo Enterprise starts, it contacts the HSM to unwrap the master key. The KEK remains protected within the HSM throughout this operation.
Before You Begin
Before configuring Fudo Enterprise, prepare the HSM environment using the standard Thales administration tools.
You will need:
an HSM service or application partition prepared for Fudo Enterprise;
the token/partition label;
the corresponding Crypto Officer (CO) PIN;
a Luna HSM Client package and credentials/certificates allowing the client to access the HSM;
network connectivity between Fudo Enterprise and the HSM service.
The HSM, its application partition, authentication policy and client credentials should be configured by the administrator responsible for the Thales environment before starting the Fudo Enterprise configuration.
Option 1: Thales Luna Cloud HSM
Create or prepare the Luna Cloud HSM service
Sign in to the Thales Data Protection on Demand portal and create a Luna Cloud HSM service, or use an existing service intended for Fudo Enterprise.
Note
When creating the service, keep FIPS restrictions enabled unless your security policy explicitly requires otherwise.
Prepare the partition that Fudo Enterprise will use and note:
the token label;
the required PIN.
Create and download a service client
Go to Services > My Services and open your service.
Click Create Service Client.
Download the resulting client package.
Note
Use the Linux x86-64 client.
The downloaded package contains considerably more functionality than Fudo Enterprise requires. It must therefore be prepared before it is uploaded to Fudo Enterprise.
Prepare the package for Fudo Enterprise
Extract the Luna client package.
Find and extract the Linux client components packaged as a
.tararchive, for examplecvclient-min.tar.Note
Do not upload the original complete client archive directly to Fudo Enterprise. Fudo Enterprise requires the selected Linux client components packaged as a
.tararchive.
Create a new
.tararchive containing the files required by Fudo Enterprise, including:libs/ plugins/ Chrystoki.conf *.pemNote
The PKCS#11 module required by Fudo Enterprise is normally
libs/64/libCryptoki2.so.
Option 2: Thales Luna Network HSM
The Fudo Enterprise-side configuration is the same as for Luna Cloud HSM, but the preparation of the Luna client package usually requires additional attention.
Prepare the HSM
Before configuring Fudo Enterprise, the Luna administrator should prepare the HSM using the standard Thales administration workflow. This includes, as appropriate:
configuring the Luna Network HSM;
configuring network connectivity;
creating or selecting an application partition;
assigning client access to the partition;
configuring authentication;
generating or installing the required client credentials and certificates;
configuring the Luna HSM Client.
The Luna administrator should then provide:
the Linux x64 Luna HSM Client files;
the associated credentials/certificates;
the token label;
the PIN required by Fudo Enterprise.
Obtain the Luna HSM Client files
Obtain the Linux version of the Luna HSM Client configured for the partition that Fudo Enterprise will use.
Note
Depending on how the Luna environment was prepared, administrators may provide the client software and the connection credentials/certificates as separate archives.
Combine all the connection credentials/certificates and the selected components from the client software archive in one directory. For example:
fudo-luna-client/
├── libs/
│   └── 64/
│       └── libCryptoki2.so
├── lock/
├── plugins/
├── Chrystoki.conf
├── Openssl.cnf
└── *.pem
Note
The number and purpose of the certificates in the archive depends on the client’s trust configuration and the HSM topology. The exact set of files depends on the Luna deployment.
Additional configuration files referenced by
Chrystoki.conf, such asopenssl.cnf, must also be included when they are required by the supplied Luna configuration.
Adjust Chrystoki.conf
Note
When the Luna Client files are moved to a different runtime environment, library, certificate and configuration paths in
Chrystoki.confmust be adjusted to the paths visible to that environment.Review
Chrystoki.confand adjust the following elements:
Change file paths.
Update any absolute paths so that they match the layout of the files inside the archive uploaded to Fudo Enterprise. For example:
/usr/safenet/lunaclient/openssl.cnfmay need to become:
Openssl.cnfSimilarly, library paths should point to the location used inside the Fudo Enterprise package, for example:
libs/64/libCryptoki2.soDisable HA logging.
In the
HAConfigurationsection, sethaLogStatus = disabled;. For example:HAConfiguration = { haLogStatus = disabled; reconnAtt = -1; AutoReconnectInterval = 60; }This disables local Luna Client HA logging while leaving the reconnect settings unchanged.
Review the Secure Trusted Channel configuration.
If the configured HSM connection does not use Secure Trusted Channel (STC), remove the Secure Trusted Channel section. This section references additional Luna Client components and identity directories that are not included in the standard Fudo Enterprise client package.
Create the Fudo Enterprise package
After adjusting
Chrystoki.conf, verify that all file paths referenced in the configuration match the actual locations of the files in the prepared directory.Package the entire prepared directory as a
.tararchive.
Configuring Fudo Enterprise
Enabling HSM protection
Note
Fudo Enterprise requires a CPU supporting the x86-64-v2 microarchitecture level (SSE4.2, SSSE3, POPCNT, CMPXCHG16B). Every physical x86 CPU since ~2009 (Intel Nehalem, AMD Bulldozer) supports x86-64-v2. If you are unable to see the Set up HSM configuration button in System > Settings, the hypervisor is presenting a generic vCPU model that masks these instructions.
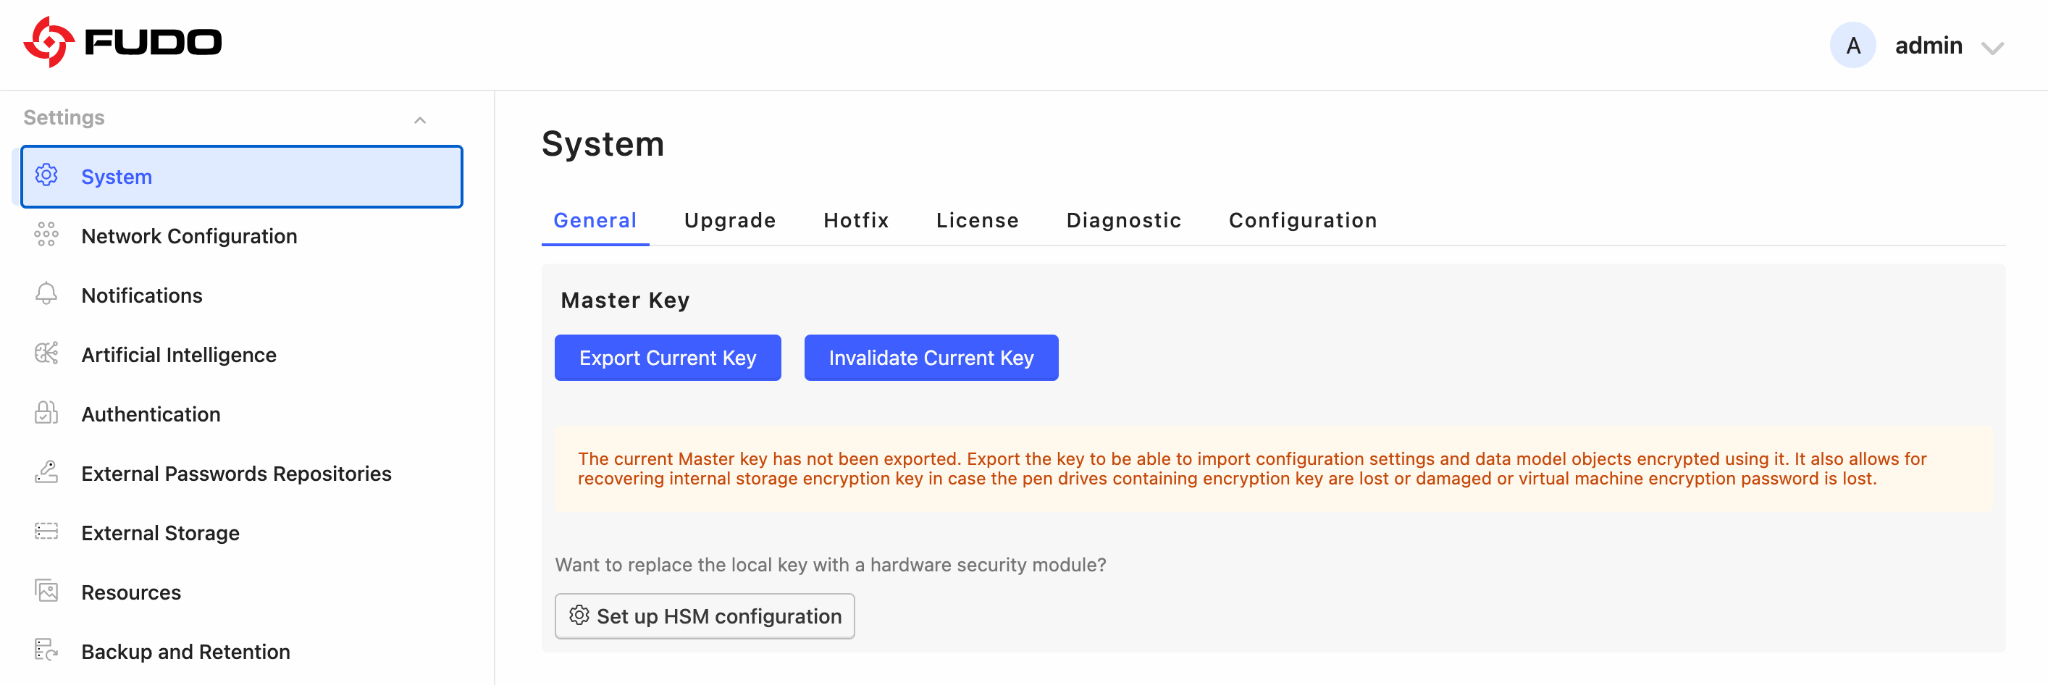
Select > .
Select the General tab.
In the Master Key section click .
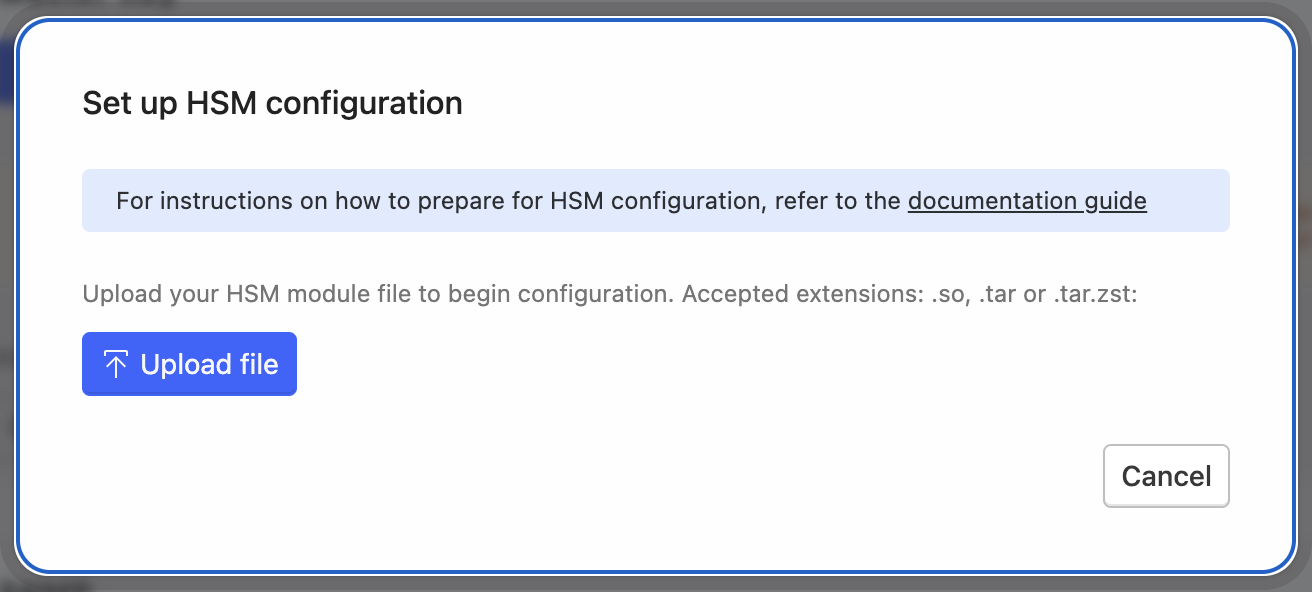
Click and select the archive prepared for your HSM client. Accepted file extensions are
.so,.tarand.tar.zst.
Configure the following fields:
Module - select the PKCS#11 library included in the uploaded package. For a standard Luna HSM client this is
libs/64/libCryptoki2.so.Token label - enter the label of the HSM partition prepared for Fudo Enterprise.
PIN - enter the Crypto Officer (CO) PIN associated with the partition.
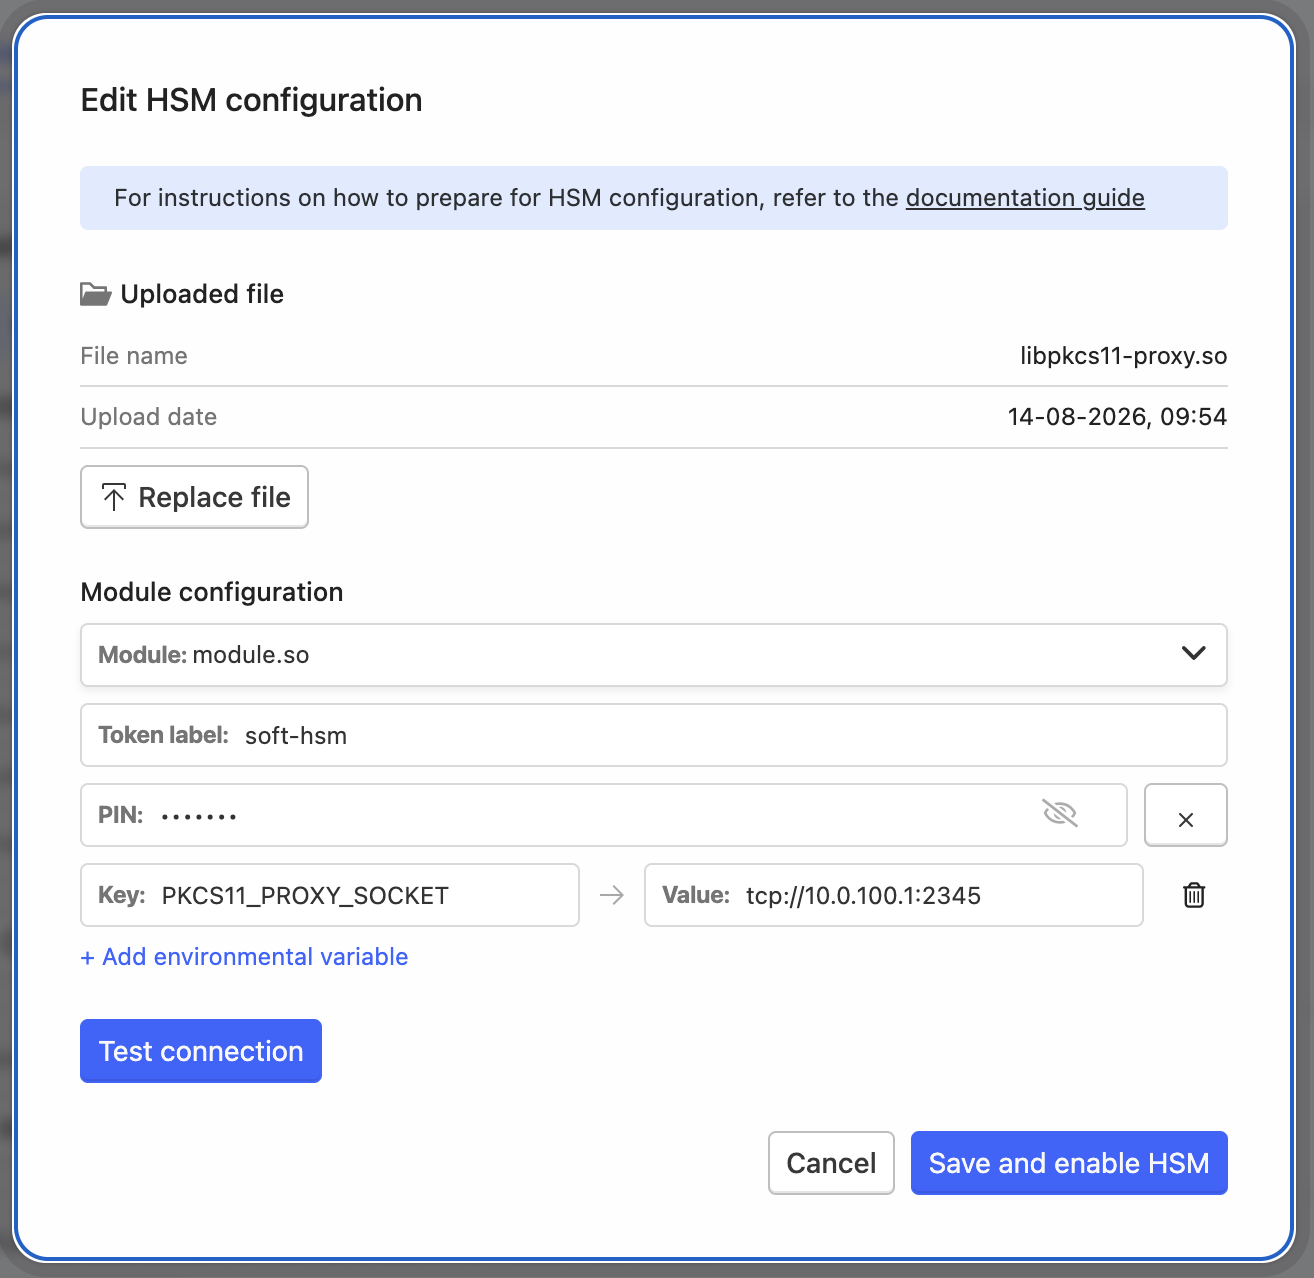
If the PKCS#11 module requires environment variables, click + Add environmental variable and provide them as Key and Value pairs.
Note
The names and values of the environment variables are defined by the documentation of the PKCS#11 module vendor.
Click to verify that Fudo Enterprise can reach the HSM with the provided credentials.
Once the test succeeds, click .
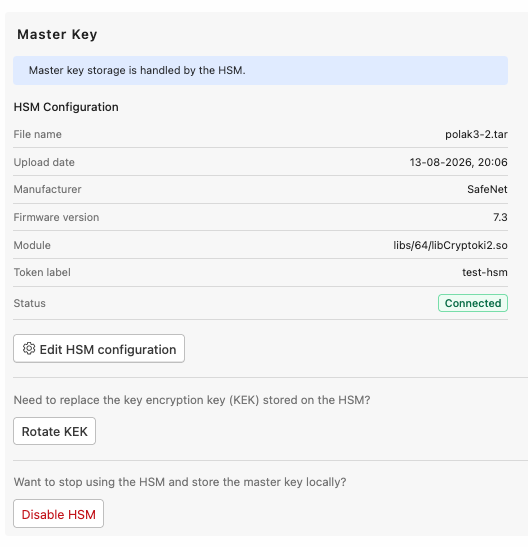
The Master Key section now displays the details of the uploaded package, the module and token label in use, and the connection status.
Rotating the key encryption key
The KEK (Key Encryption Key) is the HSM-protected key used to wrap the Master key. Rotating the KEK generates a new key encryption key on the HSM and re-wraps the Master key with it.
Note
Rotating the KEK does not change the Master key itself, so the data encrypted with the Master key is not re-encrypted.
Select > .
Select the General tab.
In the Master Key section click .
Disabling HSM protection
Disabling HSM protection unwraps the Master key and stores it locally again.
Warning
Disabling HSM protection requires access to the currently configured HSM. Do not decommission or disconnect the HSM before HSM protection has been disabled in Fudo Enterprise.
Select > .
Select the General tab.
In the Master Key section click .
Related topics: