Creating an Oracle Server [BETA]
Warning
TLS enabled is selected by default. Clear it if the monitored database does not accept TCPS connections, otherwise the connection to the server fails.
Encrypted connections are supported with the Oracle SQL*Plus client. Other client applications do not support TLS with Fudo Enterprise.
Oracle native encryption (Advanced Security Option) is refused. Configure clients so that they do not negotiate it.
Note
A server object can be linked to only one anonymous account.
A server object can be linked to only one forward account.
Accounts of the regular type are not available for Oracle servers, so password substitution cannot be used - users log in to the database with their own credentials. See Accounts.
Click + icon next to the tab of the sub-section, or
Select > and then click .
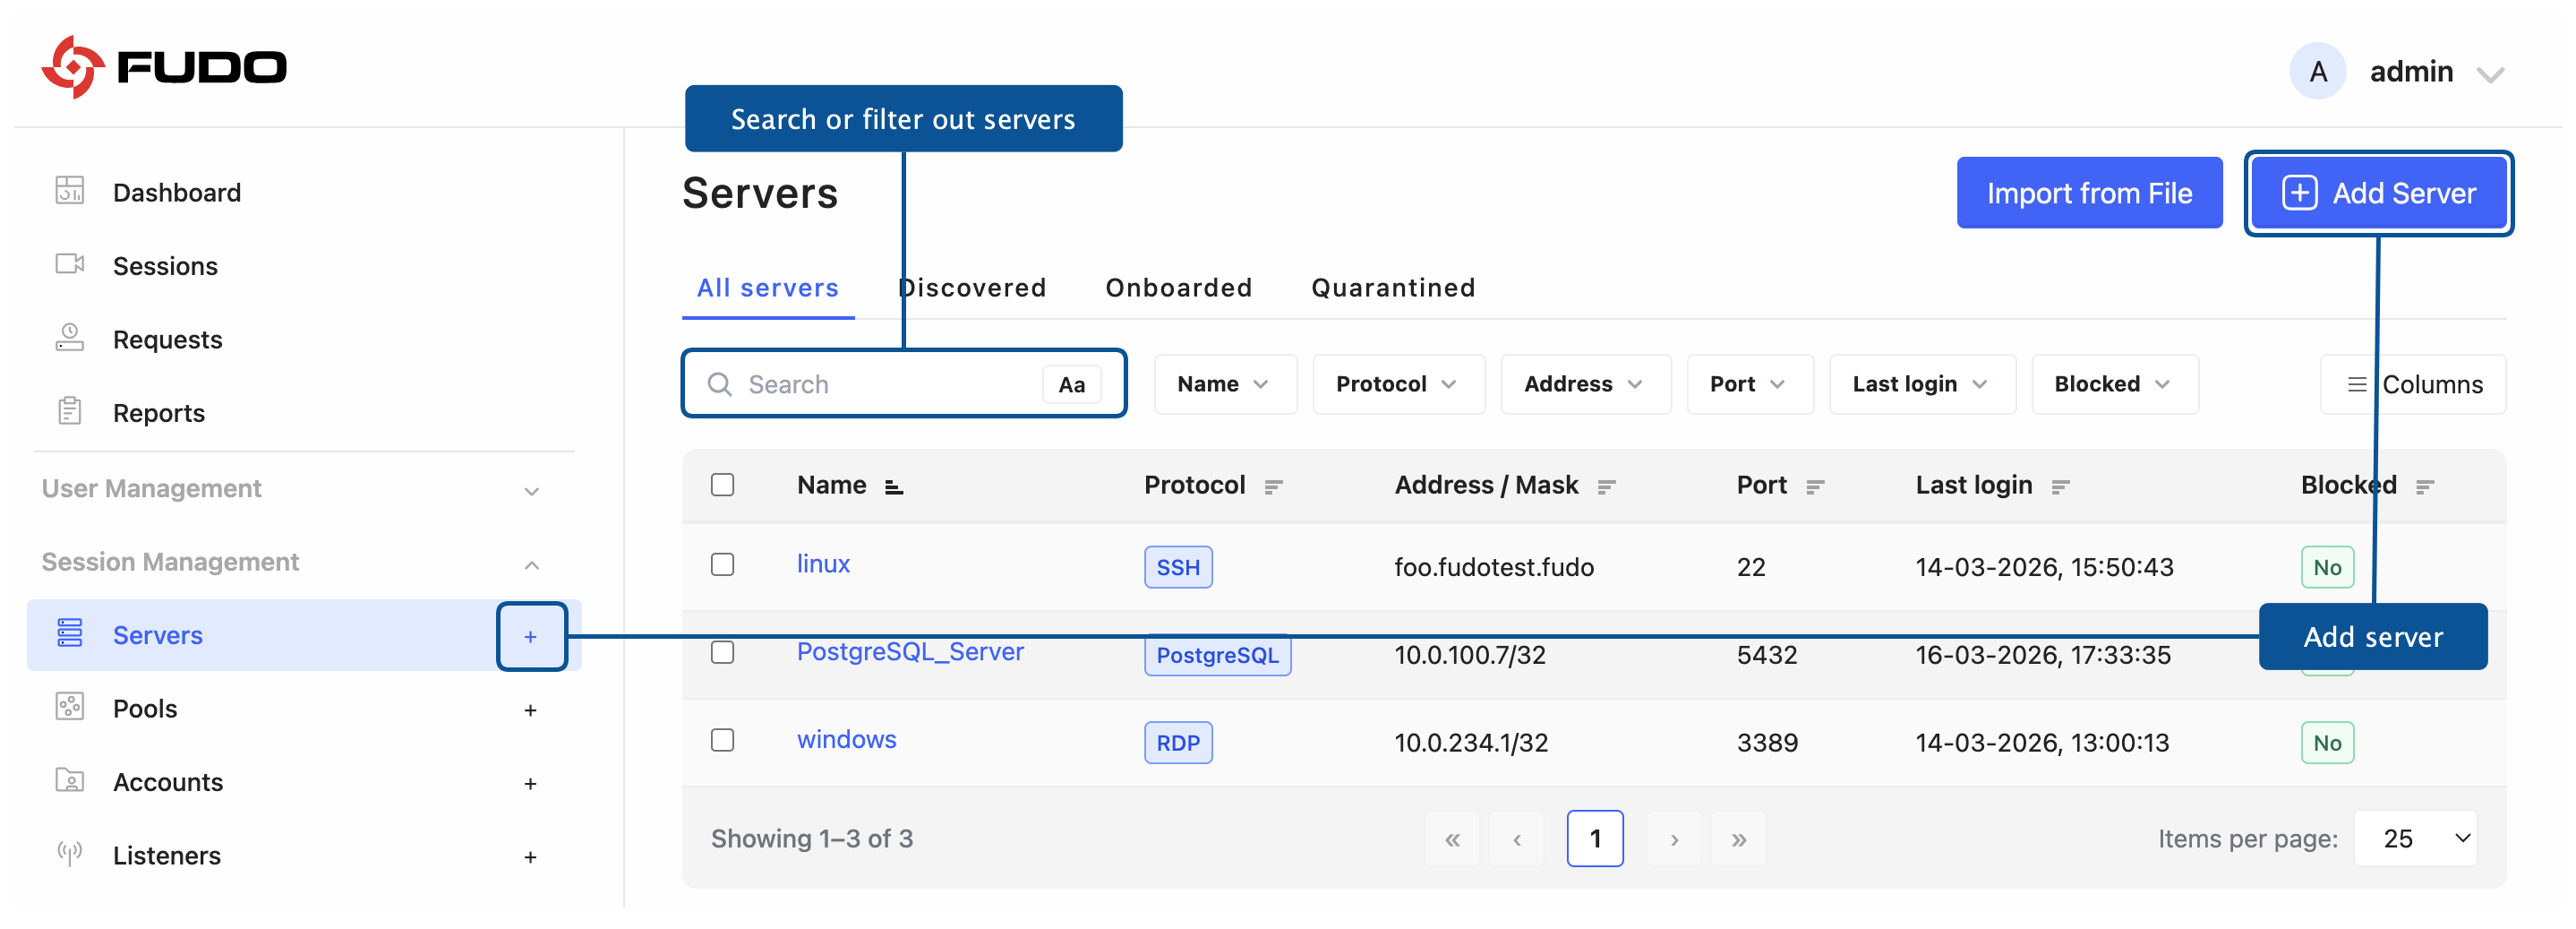
Enter server’s unique name.
Select Blocked option if the object should be unavailable after creation. A blocked server cannot be used to establish connections until it is manually unblocked. Providing a reason for blocking is required.
Optionally, click the Description checkbox and provide a text that will help identifying this server object.
SETTINGS TAB
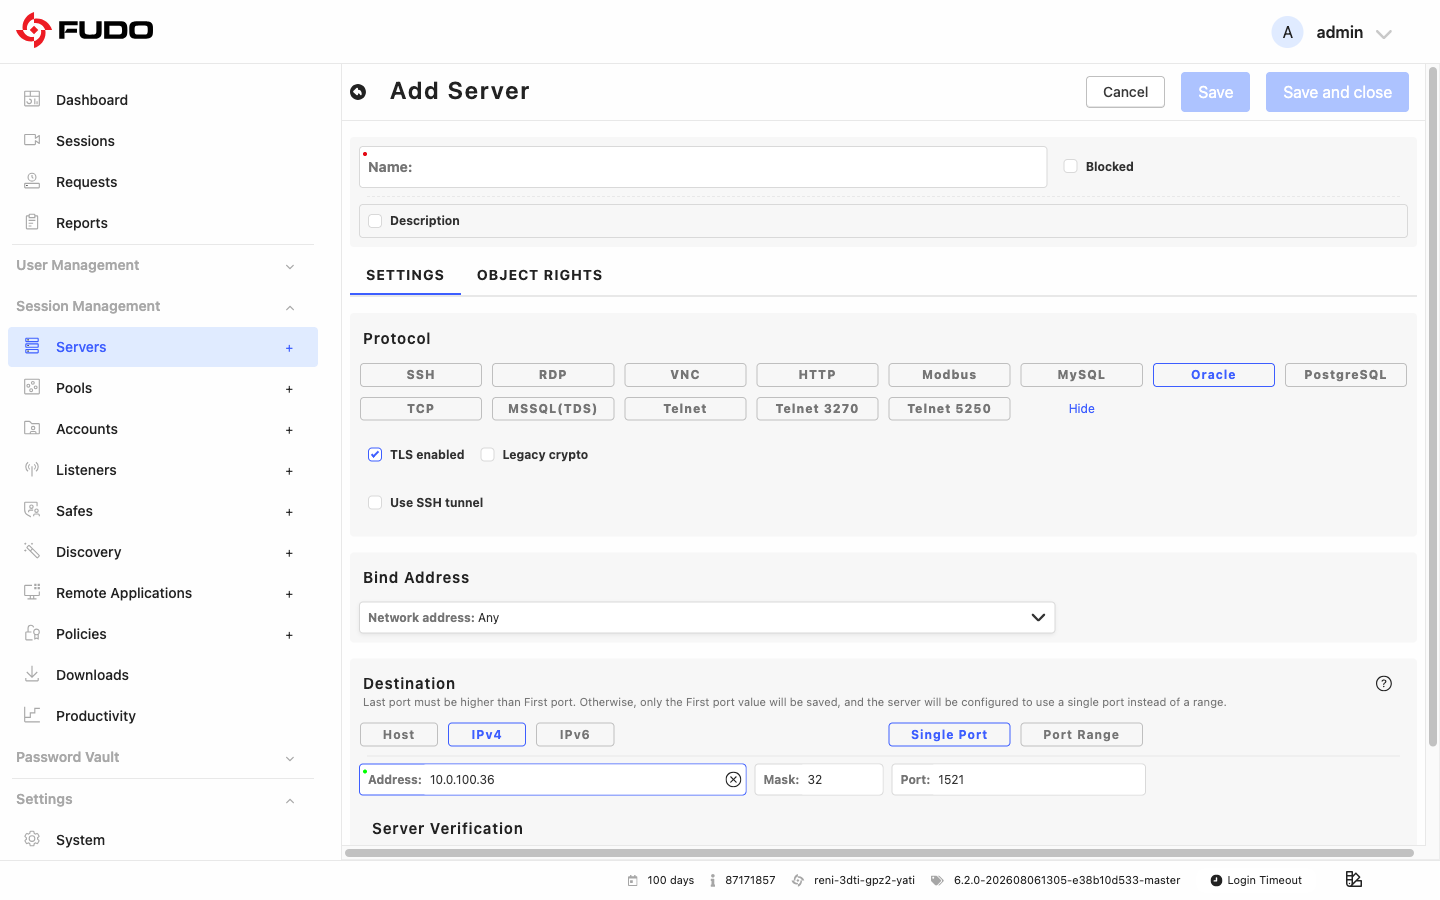
Go to the SETTINGS tab.
In the Protocol section, press the
Show allbutton and select .
Warning
After server’s definition is saved, protocol’s field is uneditable.
Clear or leave the TLS enabled option depending on whether the monitored database accepts TCPS connections.
Select Legacy crypto option to allow negotiating older encryption algorithms (DSA(1024), RSA(1024)) when establishing connections.
Select the Use SSH tunnel option and provide the SSH tunnel key to establish the connection through an SSH reverse tunnel.
If you do not use the SSH tunnel, from the Network address drop-down list, select the IP address from which connections to the monitored server will be initiated, and then configure the Destination settings.
Note
The Legacy crypto option is shown only when TLS enabled is selected.
Note
The Network address drop-down list elements are IP address defined in the Network configuration menu (Network Interfaces Configuration) or labeled IP addresses (Labeled IP Addresses).
In case of cluster configuration, select a labeled IP address from the Network address drop-down list and make sure that other nodes have IP addresses assigned to this label. For more information refer to the Labeled IP Addresses topic.
In the Destination section, define the address of the target server:
Select , , or ,
Enter the Address. The Port field is filled in with the Oracle default
1521; change it if the database listens on a different port.
In the Server Verification section, specify the server verification method:
Select to verify the server based on its certificate,
Select to verify the server certificate using a trusted certificate authority,
Select to disable server certificate verification.
If you select , the Verify hostname option is also available and checked by default. It additionally checks that the server certificate covers the configured server address (host name or IP address); if it does not, the connection to the server fails. Clear the option to verify the certificate against the CA certificate only, for example when the certificate was issued for a name other than the configured address.
Click .
OBJECT RIGHTS TAB
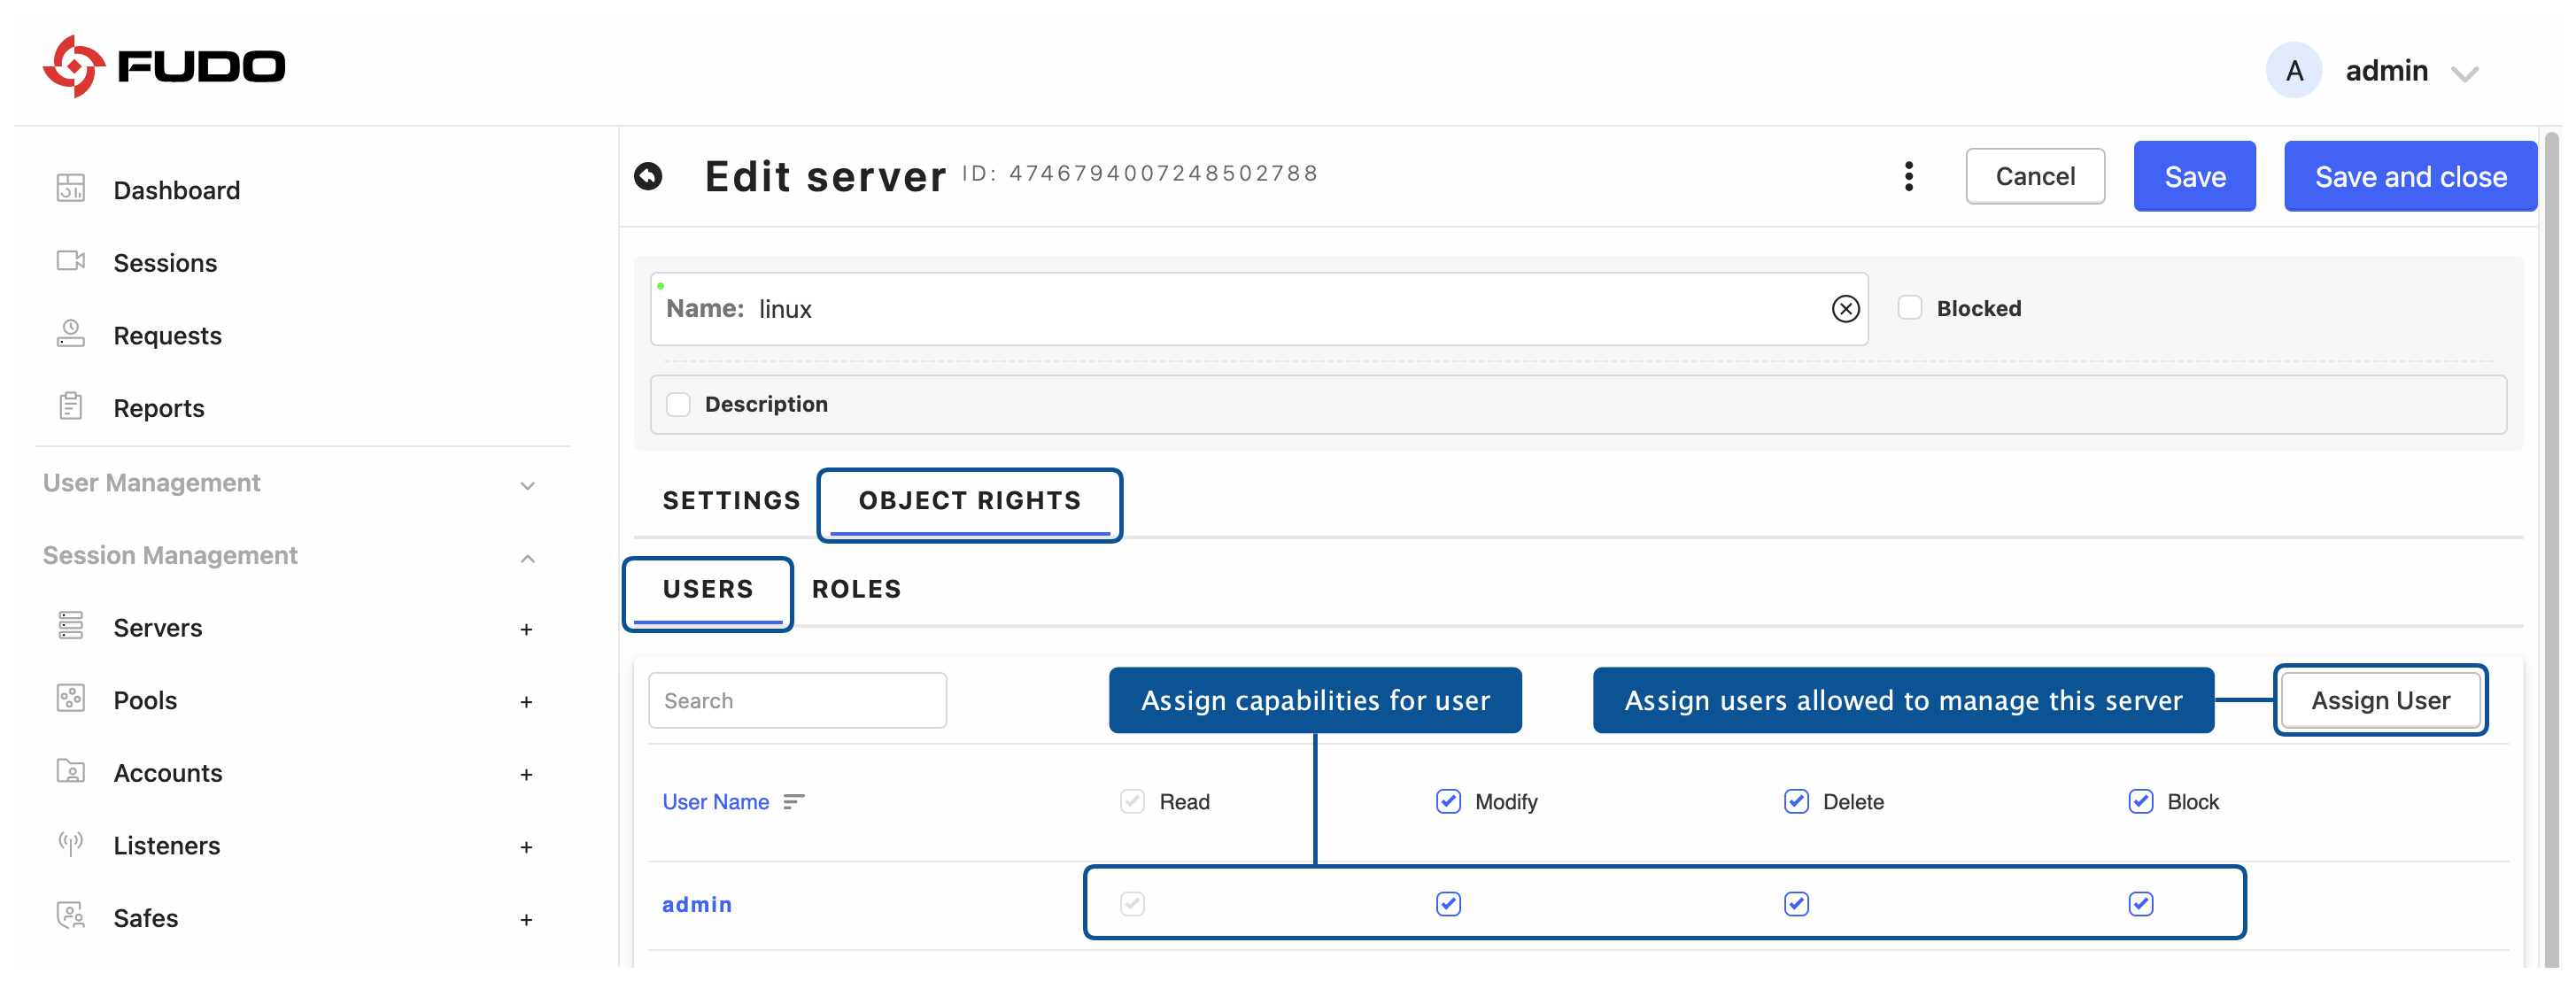
The OBJECT RIGHTS tab is used to define which users and roles are allowed to manage the object and which capabilities (Read, Modify, Delete, Block) are assigned to them.
Go to the OBJECT RIGHTS tab.
Open the USERS sub-tab.
Click , select the users from the list, and click .
In the Users list, select the capabilities for each user by enabling the options available for the given object, such as Read, Modify, Delete, or Block.
Open the Roles sub-tab.
Click , select the roles from the list, and click .
In the Roles list, select the capabilities for each role by enabling the options available for the given object, such as Read, Modify, Delete, or Block.
Related topics: