Custom Secret Changers
Custom secret changers enable defining a set of commands executed on a remote host in case the built-in secret changers cannot handle a specific use case scenario. Secret changers can be configured to manage either user account passwords or SSH keys, depending on the selected object target.
Note
In cluster configuration, the node responsible for changing passwords on monitored systems is configured in system settings. For more information refer to Secret Changers - Active Cluster Node topic.
Defining a Custom Secret Changer
Click + icon in the main menu next to the tab, or
Select > and click .
Note
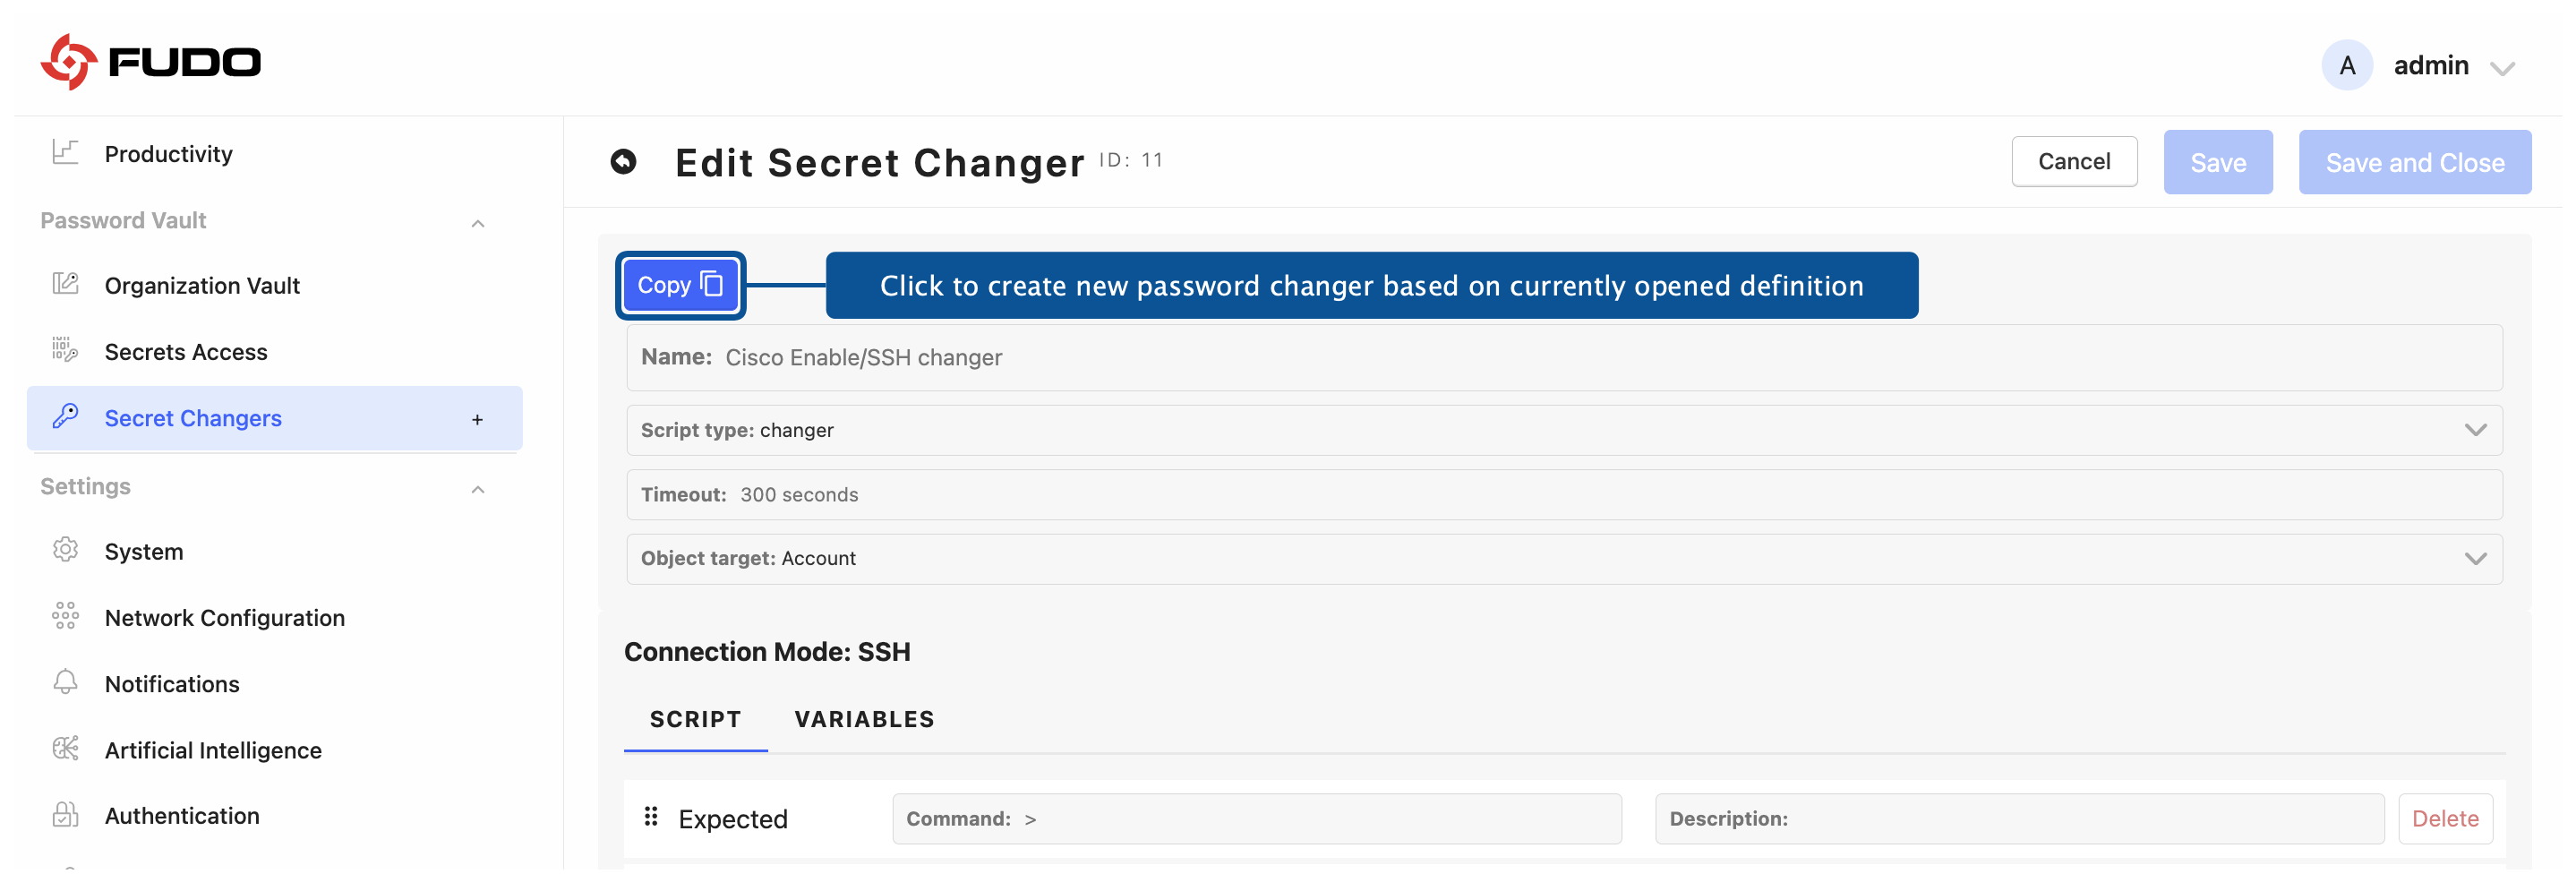
Alternatively, you can edit existing secret changer and click to create a new secret changer based on currently opened definition.
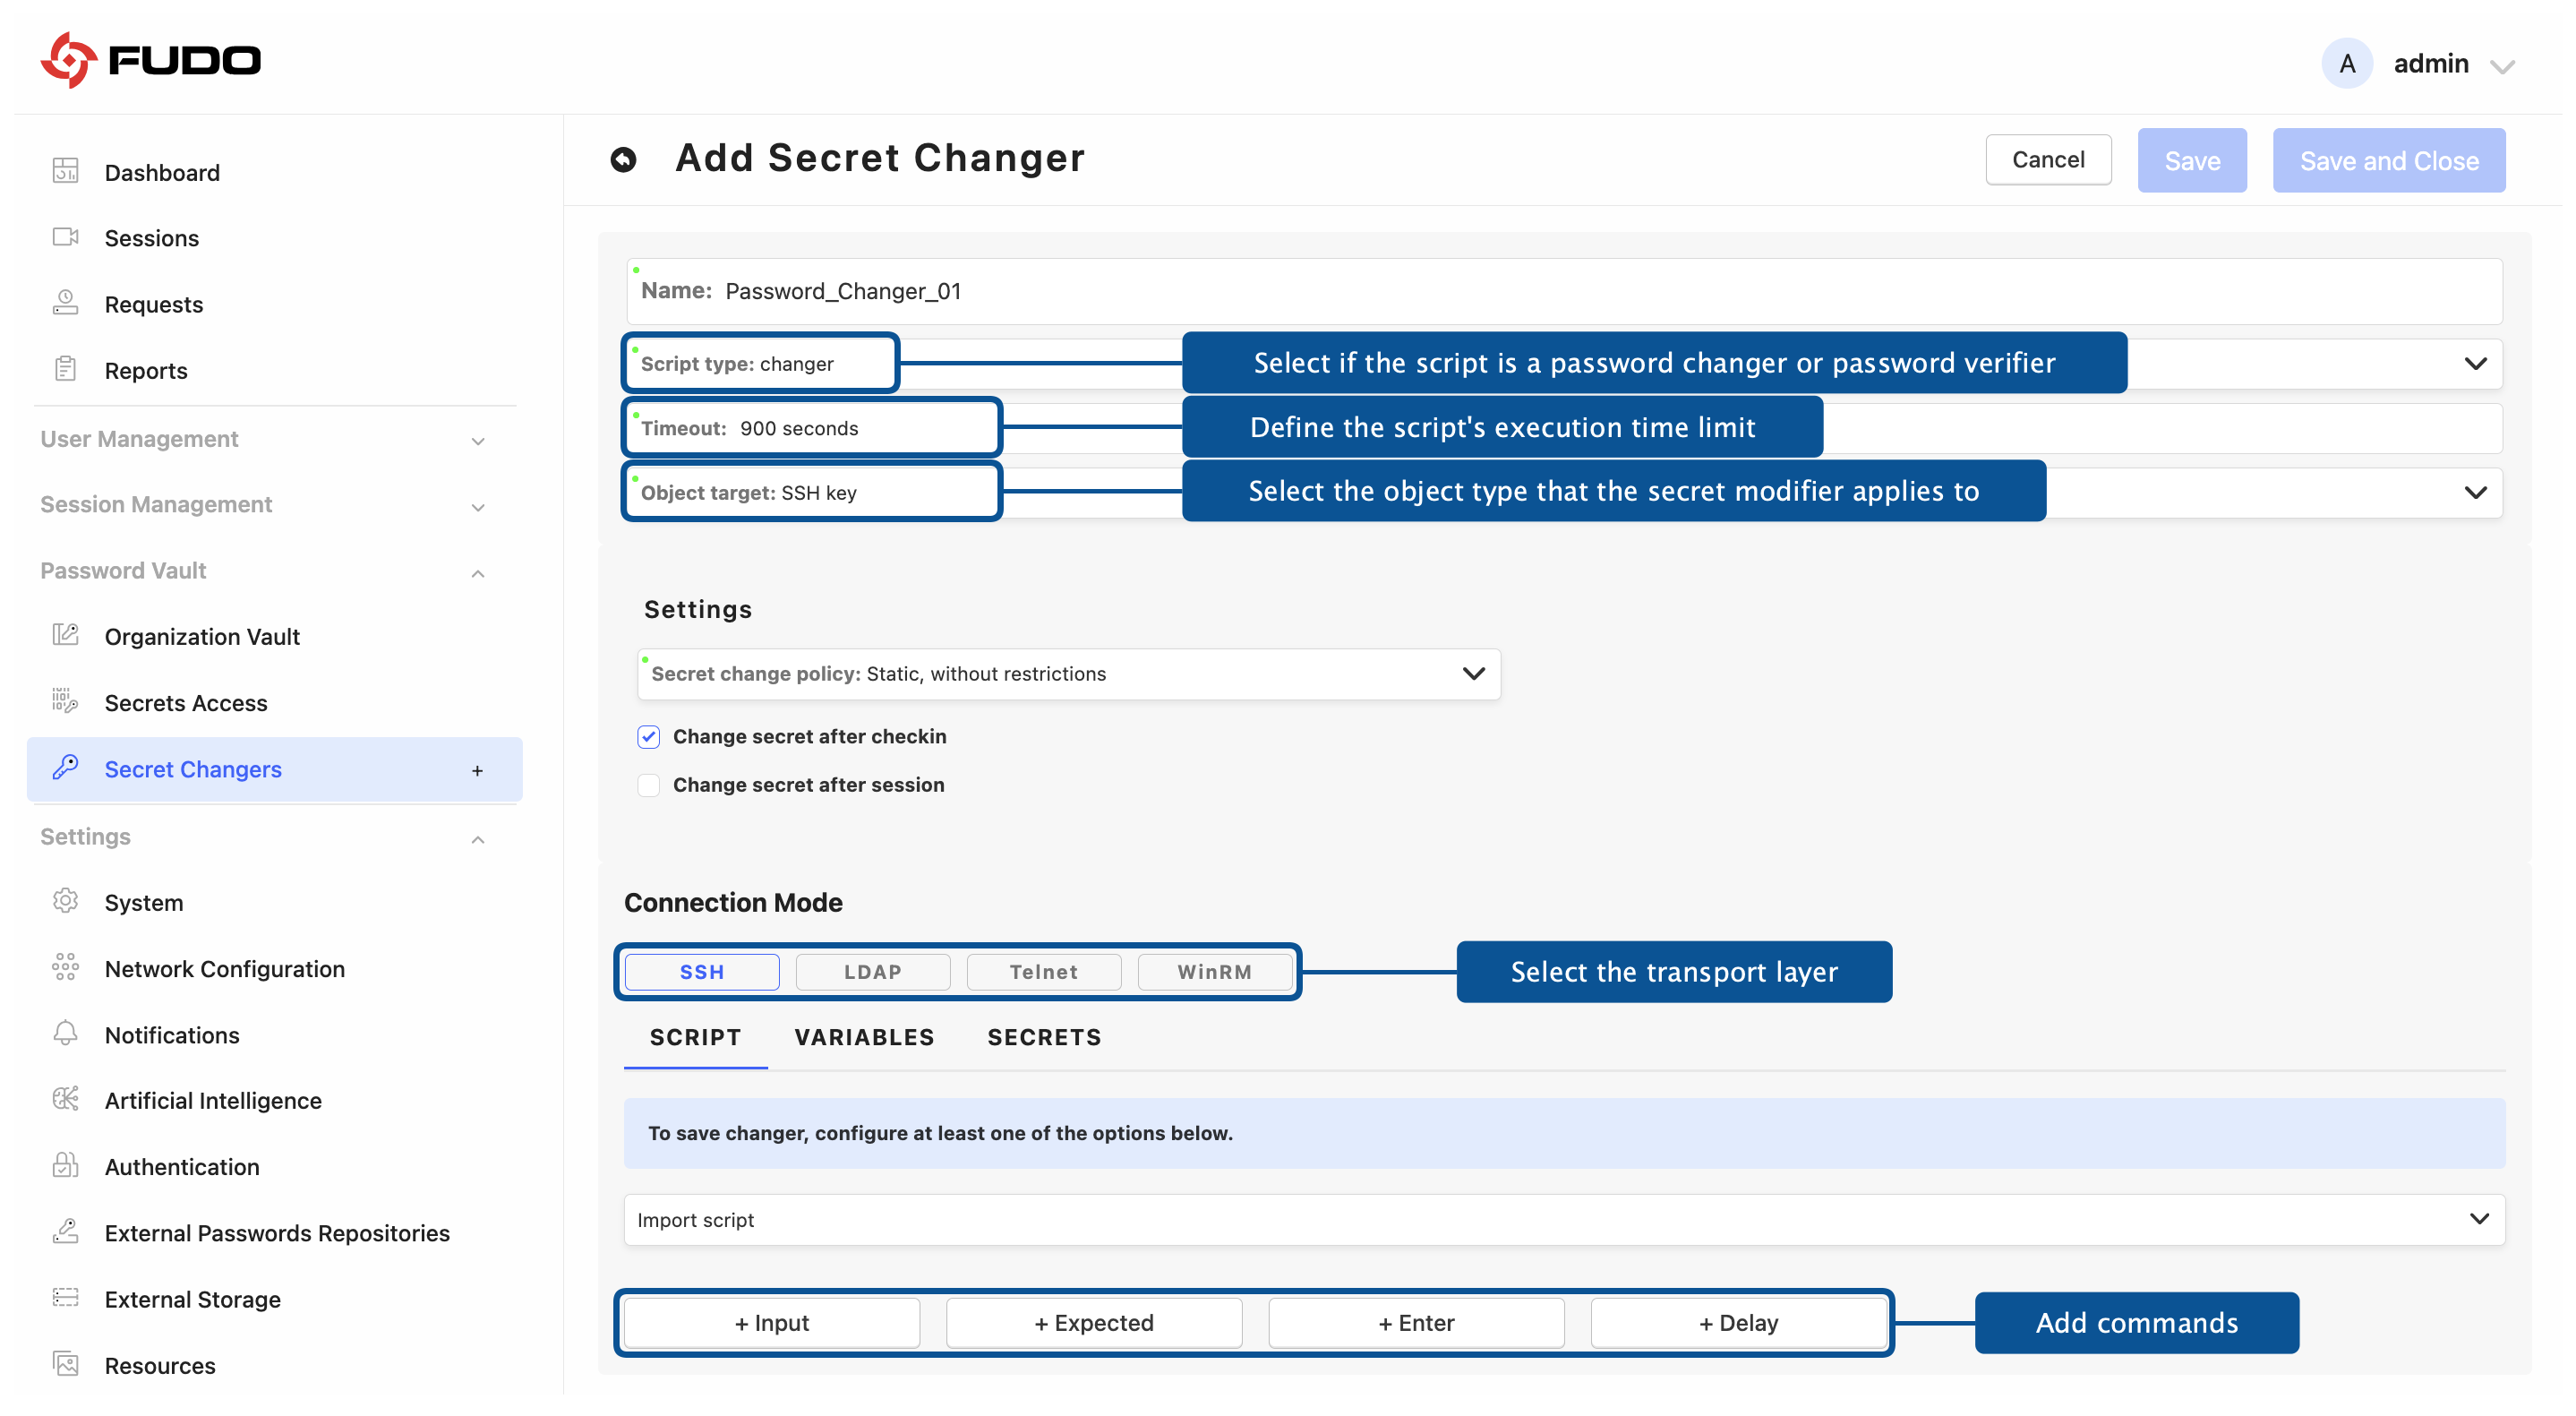
Define the secret changer’s name.
From the Script type drop-down list, select if the script is a secret changer or Secret verifier.
In the Timeout field, define the script’s execution time limit.
From the Object target drop-down list, select the target type:
Password - Manages a Login (password) secret stored in the Password Vault.
SSH key - Manages an SSH Key secret stored in the Password Vault.
Account - Manages the secret of a monitored account; assigned in the account’s SECRET CHANGERS tab.
If the object target is Password or SSH key, the Settings section appears. From the Secret change policy drop-down list, select a policy.
Optionally, enable Change secret after checkin and Change secret after session.
Note
A Secret change policy defines settings shared by both changers and verifiers, so one policy can describe how a secret is changed and how it is verified. Selecting a policy here does not enable verification on its own - the secret is verified only when a secret verifier is also assigned to the secret in its Changers tab. If only a changer is assigned, the secret is changed but not verified, even when the policy includes verification settings.
In the Connection mode section, click , , , or to select the transport layer.
In the SCRIPT tab, click one of available options to add a command.
Note
Available commands depend on selected transport layer. For more information on connection modes, refer to the Connection Modes topic.
- command executed on target host.
- expected result.
- delay between commands’ execution.
- directory service DN (Distinguished Name) parameter.
- directory service user filter.
Warning
To handle a secret change, you must use an account (
transport_loginandtransport_secret) that has delegated Reset user passwords and force password change at next logon permissions for the Organizational Unit (OU) containing the users whose passwords will be changed, or the account must be a member of the Account Operators group.To configure WinRM secret changers, you need to provide user credentials with the authority to change passwords (typically an admin-level account). However, it’s important to avoid using this account to change its own password, as WinRM will return an error that Fudo Enterprise cannot process. Make sure that the ``account_login`` and ``transport_login`` variables are set to different values.
Enter the command or define action’s parameters.
Note
You can use pre-defined transport layer or user defined variables in commands. To use or define a variable, enclose it in %% characters (e.g. %%transport_host%%, %%custom_variable%%).
Repeat steps 10-11 to add more commands.
In the Variables tab, define variables’ attributes.
Note
Variables can be initiated with values referenced from other objects or they can be assigned a constant value.
Predefine the property values so that the secret changer assigned to the account during the Discovery process will not require any additional configuration.
Click .
Password Changer Configuration Example
In this secret changer example, the password change is triggered with the passwd command executed with sudo privileges on a host running FreeBSD operating system.
Commands list
Action |
Content |
Comment |
|
|---|---|---|---|
1 |
EXPECTED |
|
Expected terminal output with a ‘Password’ word in it. |
2 |
INPUT |
|
A value of the |
3 |
EXPECTED |
|
Expected terminal output within given regular expression. |
4 |
INPUT |
|
Change password for account where |
5 |
EXPECTED |
|
Expected terminal output with ‘Password’ word in it. |
6 |
INPUT |
|
A value of the |
7 |
EXPECTED |
|
Expected terminal output with ‘Changing local password’ phrase in it. |
8 |
EXPECTED |
|
Expected terminal output with ‘New Password’ phrase in it. |
9 |
INPUT |
|
A value of the |
10 |
EXPECTED |
|
Expected terminal output with ‘Retype New Password’ phrase in it. |
11 |
INPUT |
|
A value of the |
12 |
INPUT |
|
|
13 |
EXPECTED |
|
Variables
Variable name |
Object type |
Object property |
Encrypt |
|---|---|---|---|
transport_method |
constant |
|
|
transport_bind_to |
server_property |
bind_ip |
|
transport_user |
account |
login |
|
transport_host |
server_address_property |
host |
|
transport_port |
server_property |
port |
|
transport_secret |
account |
secret |
|
transport_host_public_key |
constant |
|
|
account_login |
account |
login |
|


Editing a Custom Secret Changer
Select > .
Click the name of desired secret changer.
In the Script tab, edit selected commands.
Click to remove selected command.
Click .
Deleting a Custom Secret Changer
Select > .
Select custom secret changer and click .
Confirm deleting selected objects.
Related topics: