Events Log
System log is an internal registry of users activities which influence system state (login information, administrative actions, etc.). Please refer to the Log Messages section for a list of key log messages.
To display system log contents, select > .
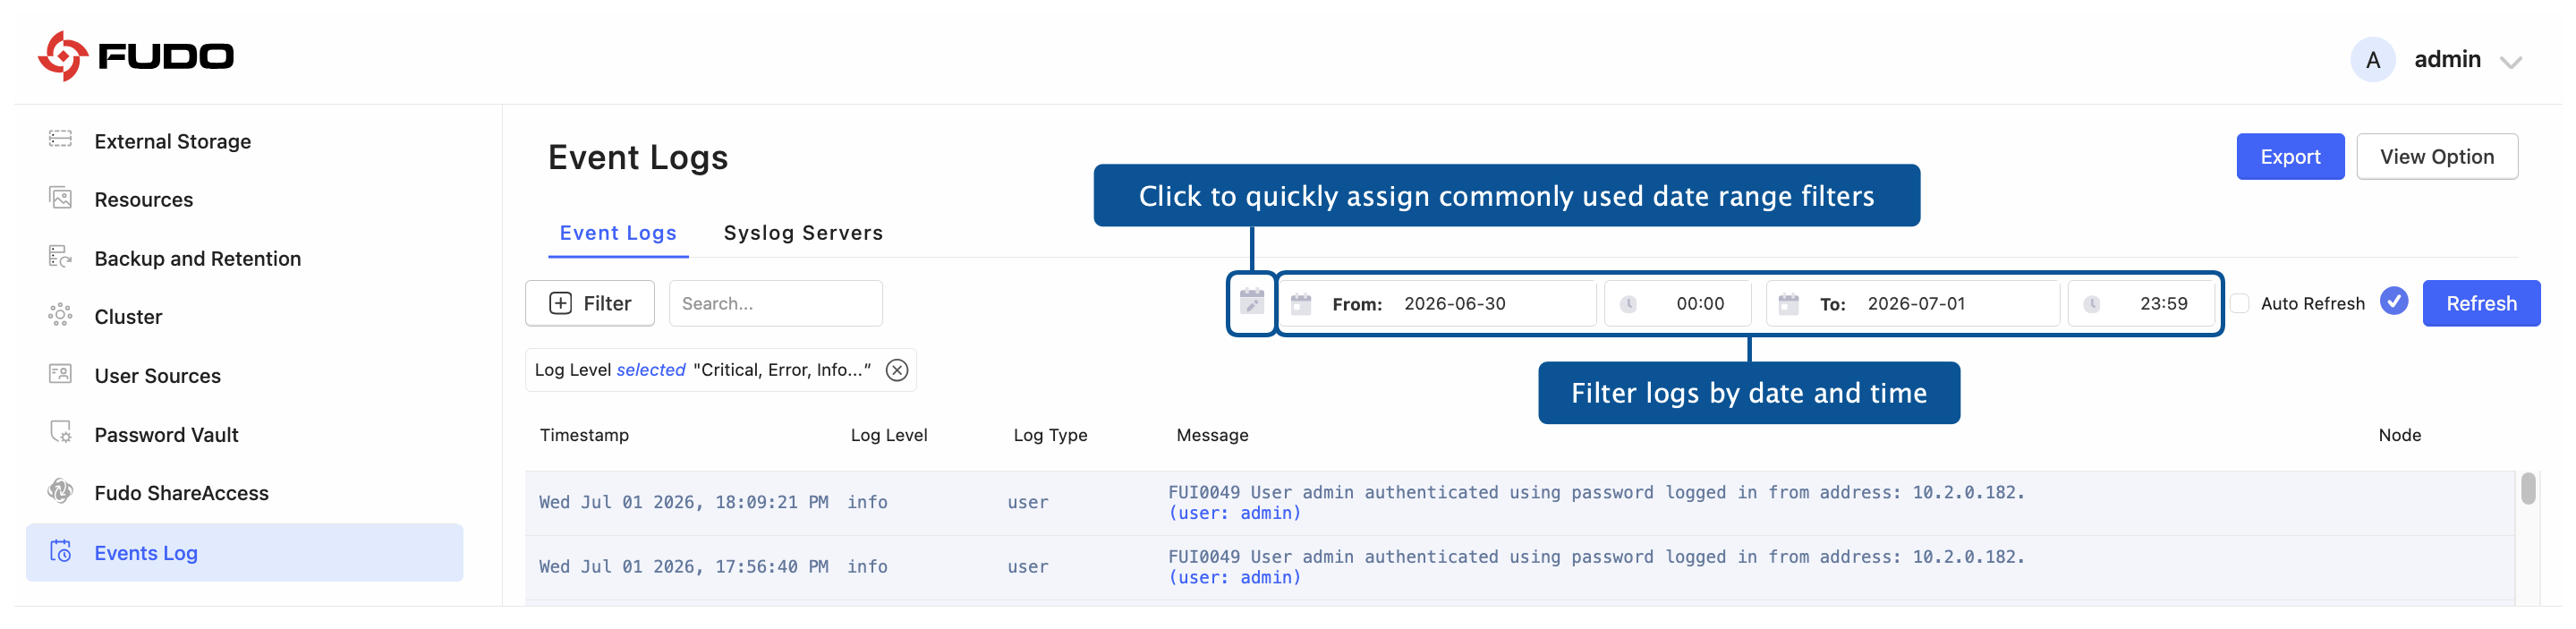
Filtering Logs by Date and Time
Logs can be filtered by date and time directly from the date bar located above the log list. Additionally, there is a set of commonly used date range filters, such as Today, Last 24 Hours, This Week, Last 1 Hour, Last 1 Year, etc., accessible through the calendar icon.
External Syslog Servers
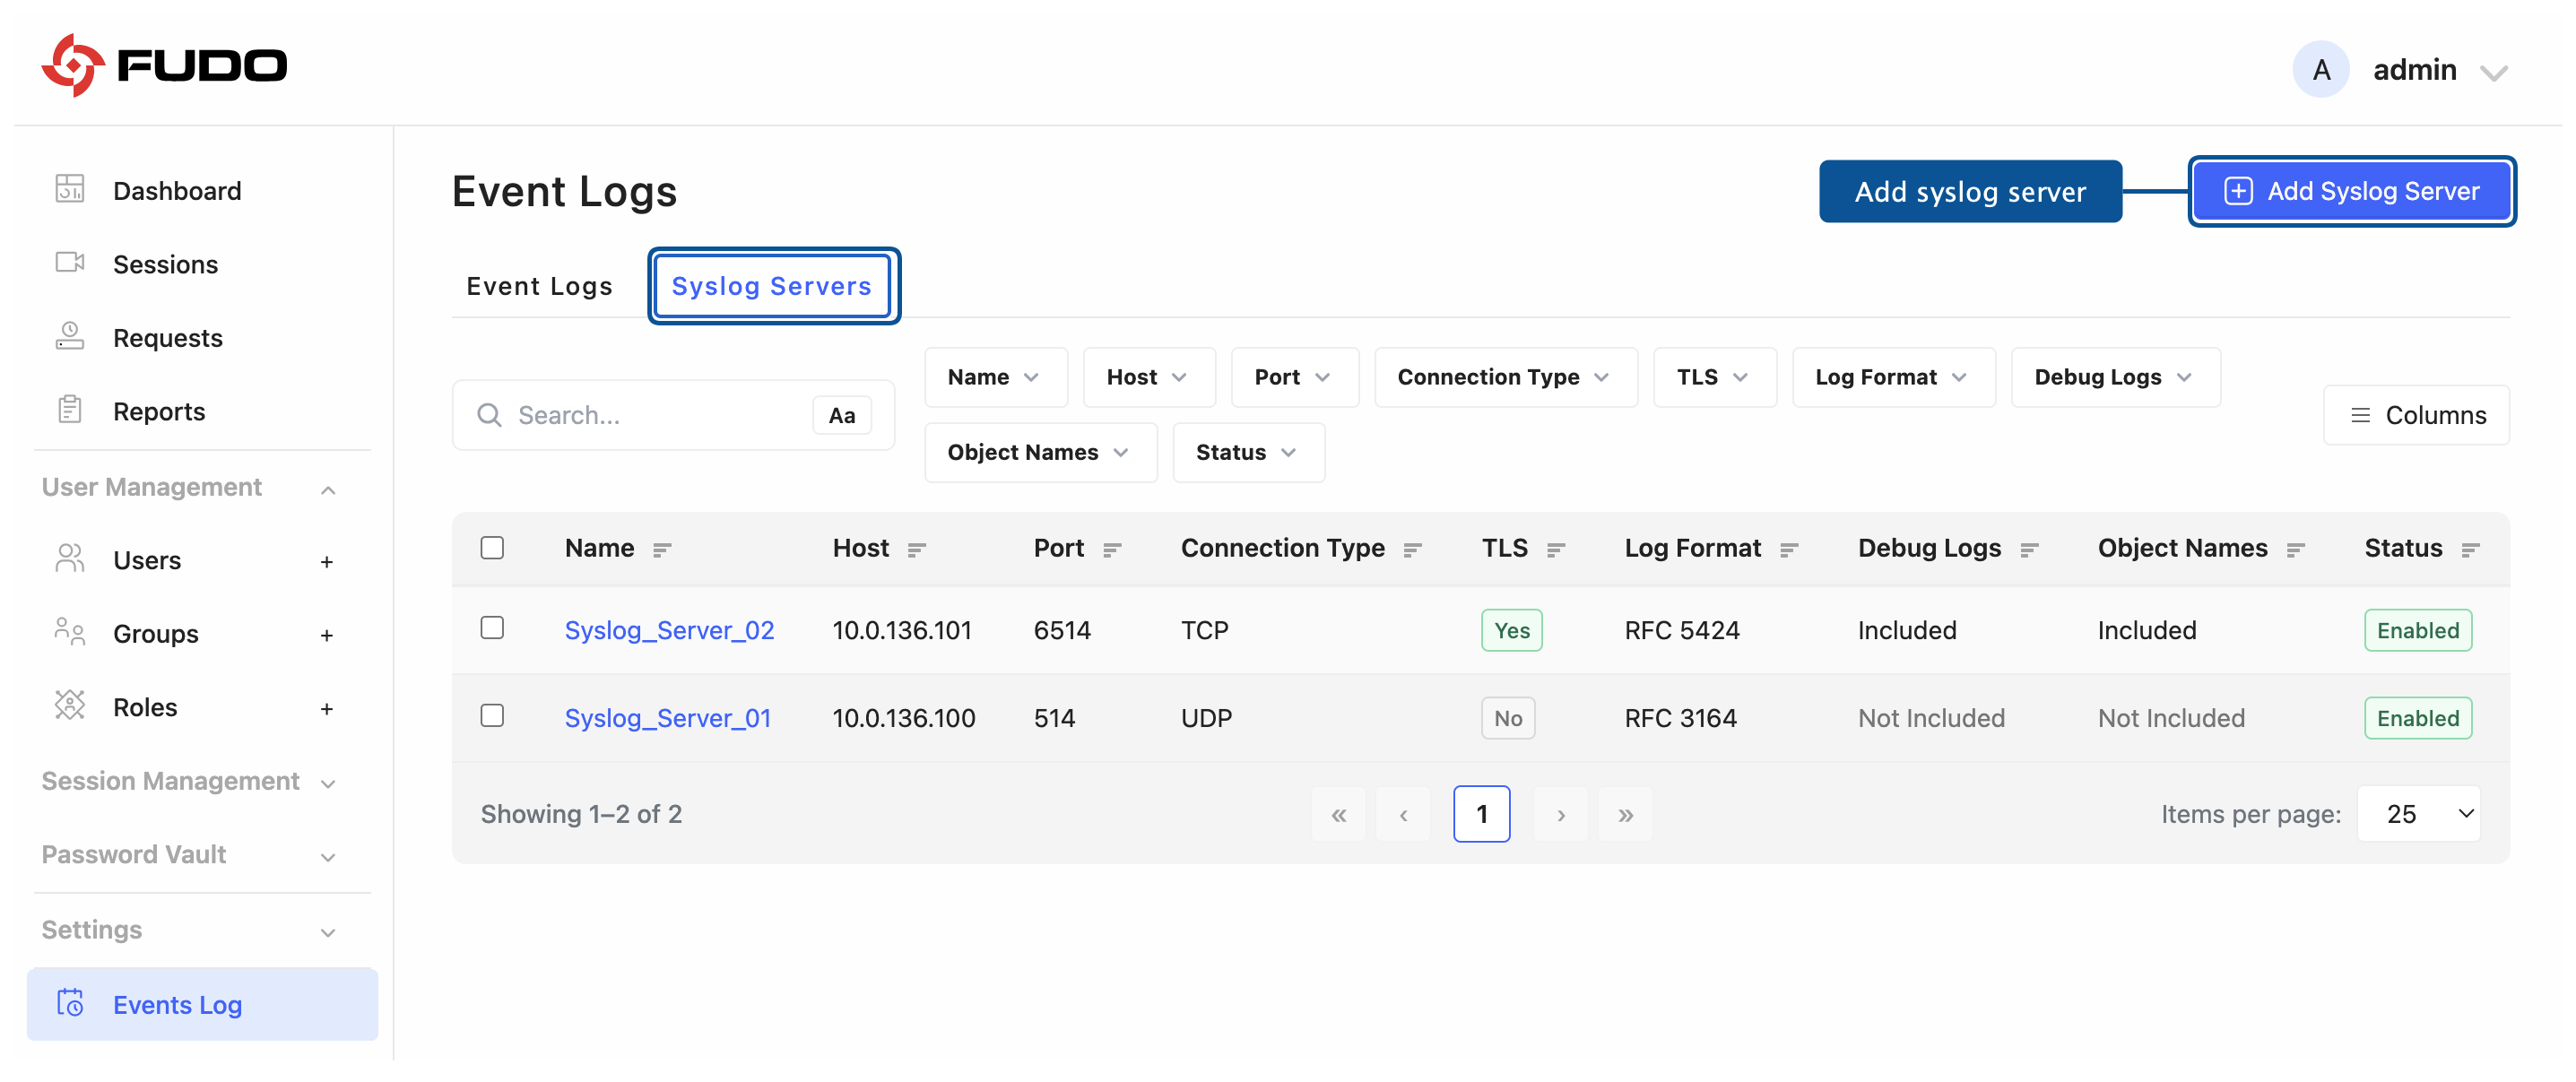
Fudo Enterprise can forward event log entries to external Syslog servers. Configured servers are managed in the dedicated Syslog Servers view, available under > . The view lists each configured server together with its name, host, port, connection type, TLS status, log format, whether debug logs and object names are included, and whether the server is enabled.
Note
Fudo Enterprise can communicate with syslog servers over the UDP or TCP transport. TLS encryption is available for connections that use the TCP transport.
Event log entries can be forwarded in the RFC 3164 (BSD, default) or the RFC 5424 format. The log format is selected individually for each server.
Messages are sent to the syslog server through the network interface that has the Admin Panel purpose selected in the network configuration. The IP address used must either be able to reach the target host’s network directly or use the default gateway. For more information, refer to the Network Interfaces Configuration section.
During an upgrade from version 6.0 or earlier, an existing syslog configuration is automatically migrated to the new syslog server model as UDP syslog servers using the RFC 3164 log format.
Adding a Syslog Server
To add a Syslog server, proceed as follows.
Select > .
Open the Syslog Servers tab and click .
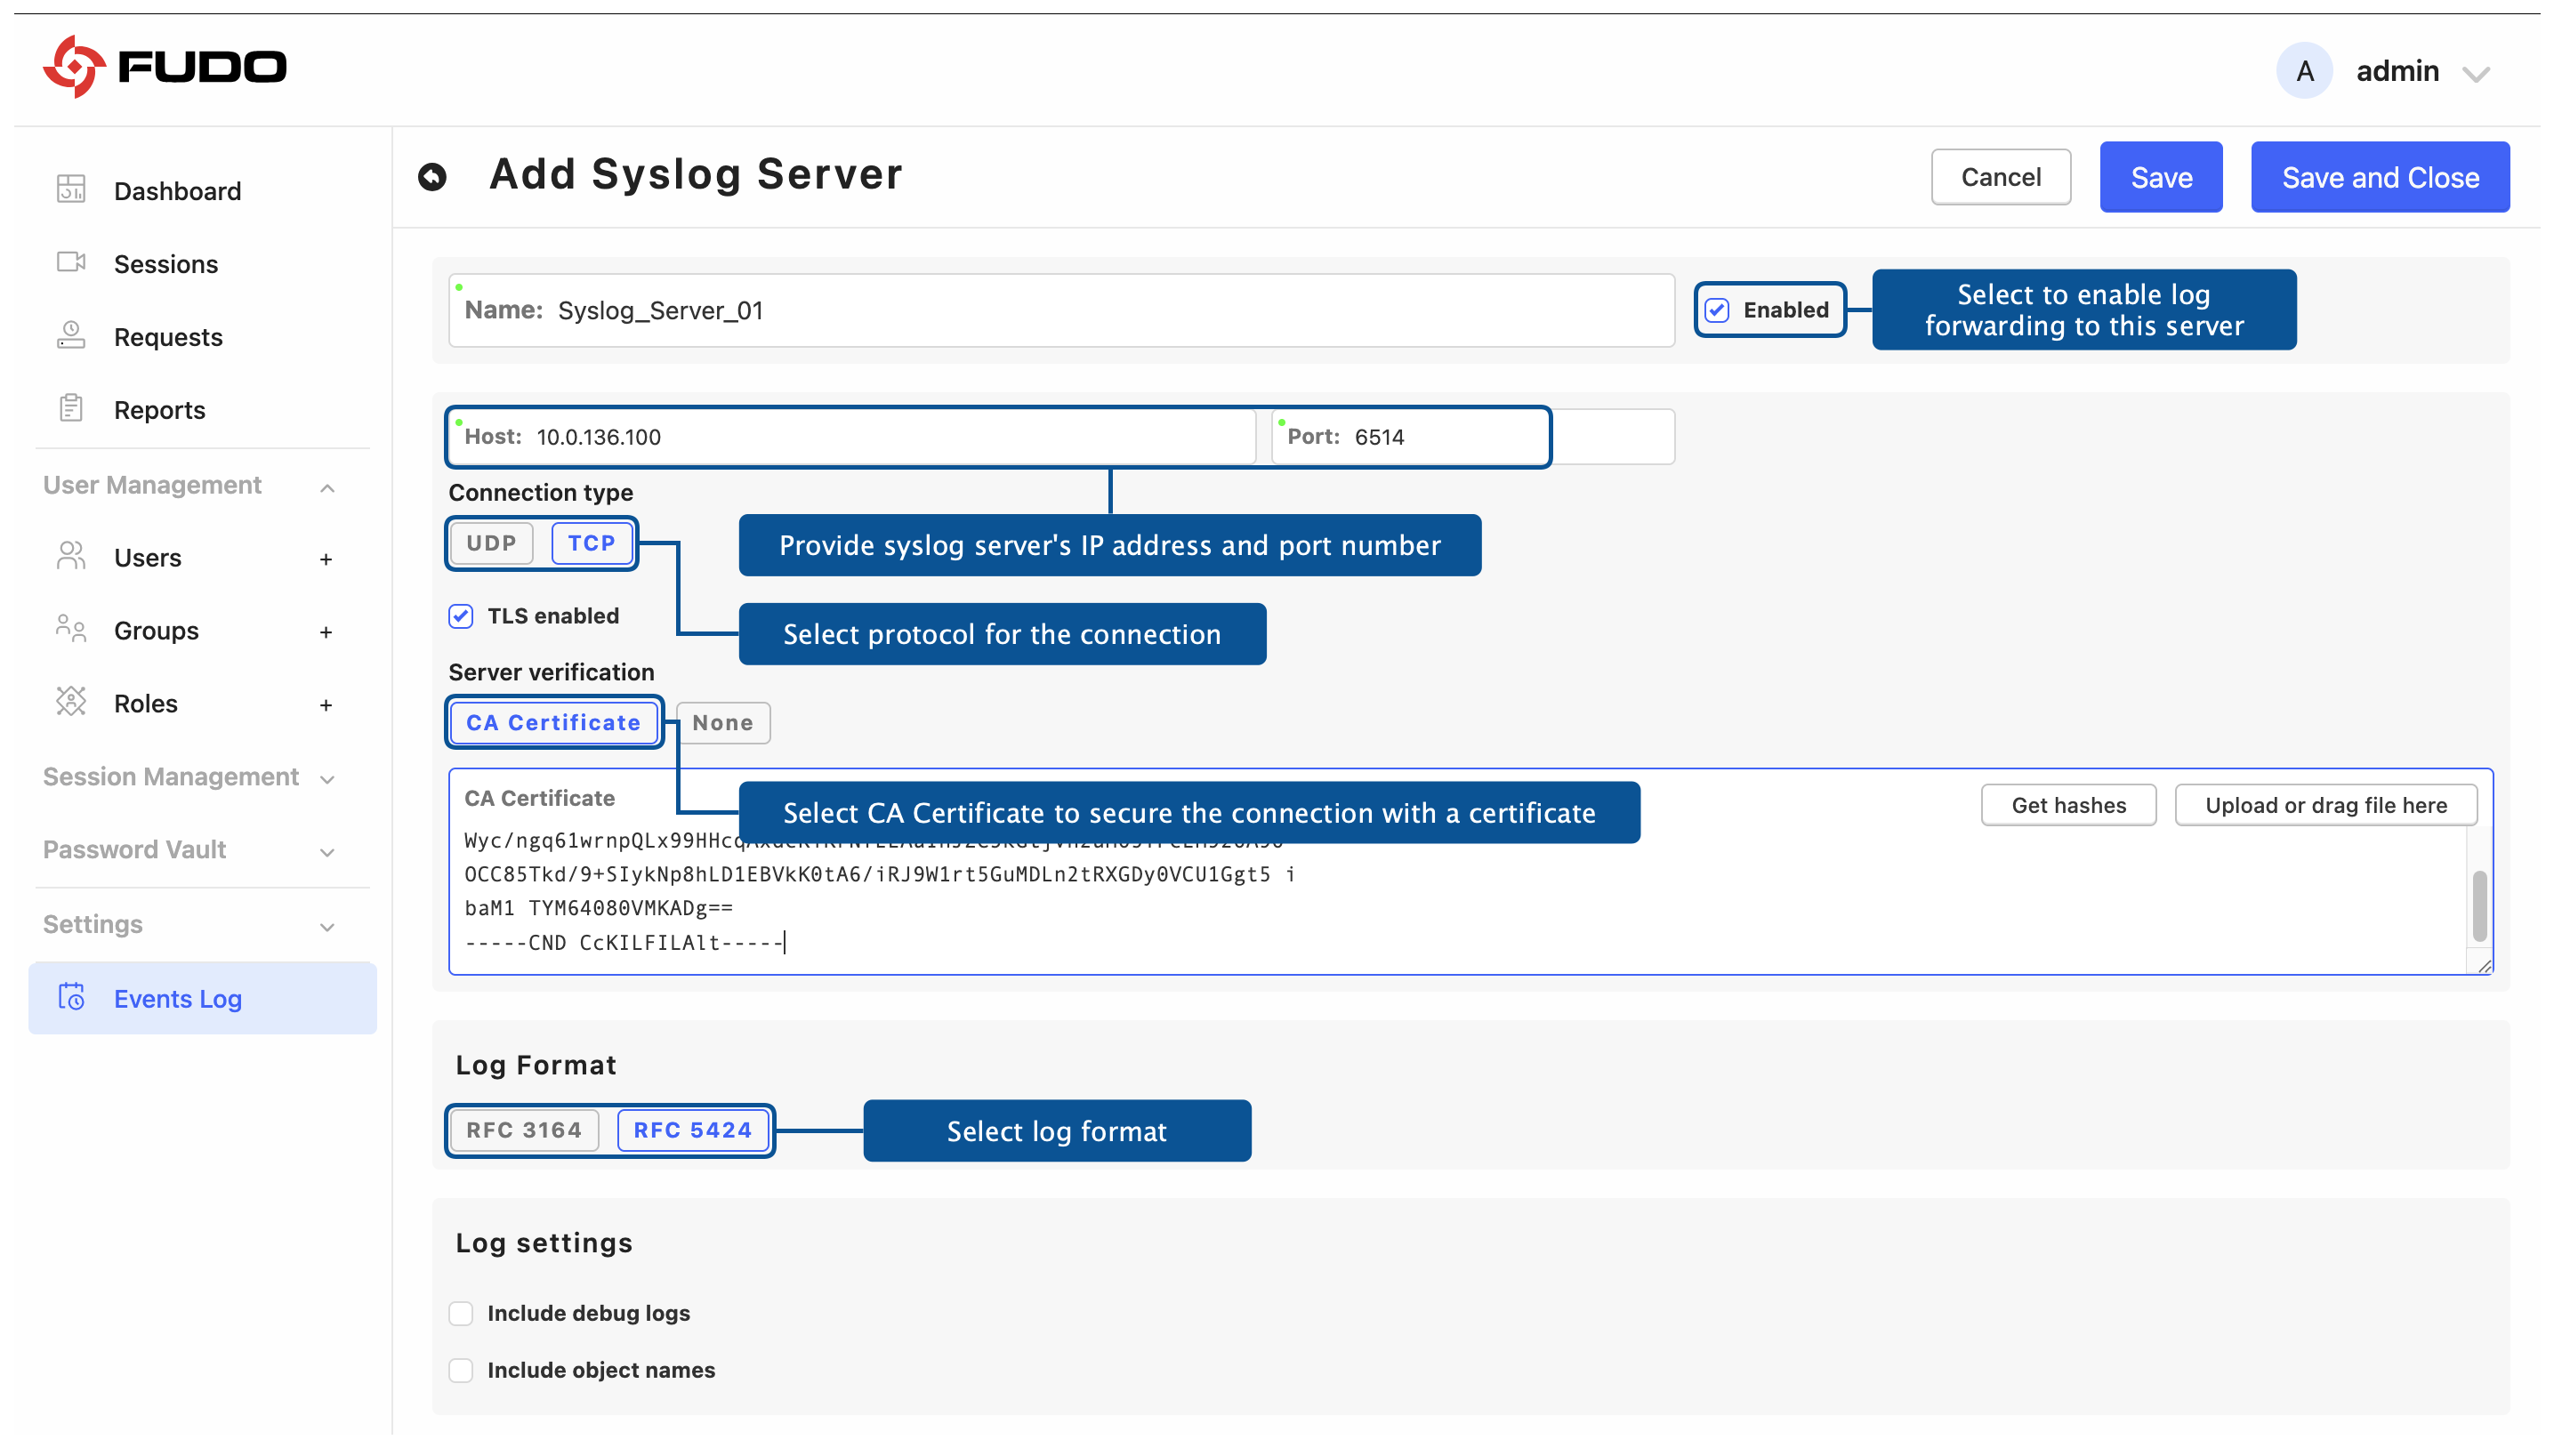
In the Name field, enter a unique name for the server.
Provide the server’s Host and Port (the default port is 514 for UDP and 6514 for TCP connections).
Set Connection type to or .
For a TCP connection, select TLS enabled to encrypt the transmission. Under Server verification, select to secure the connection with a certificate and paste or upload it in the field below, or select to connect without verification.
Under Log Format, select to send messages in the BSD format, or to send them in the RFC 5424 format.
Optionally, under Log settings, select Include debug logs and Include object names.
Make sure the Enabled option is selected to activate log forwarding to this server.
Click .
Note
Log entries sent to syslog servers that use the RFC 3164 log format are formatted as follows:
[level] TIMESTAMP TAG[PID]: MESSAGEwhere:
level– log level (optional),TIMESTAMP– time of the log entry,TAG– application name, alwaysfudo,PID– process ID,MESSAGE– the actual log message, preceded by the component or module name.
Example:
May 29 05:51:08 fudo[49411]: [INFO] (api) (type: admin) (subject:9034220852505214977) (fudo_user: 9034220852505214977) (fudo_safe:9034220852505214977) FAI0876 Administrator admin connected safe main touser admin at position 0.For servers that use the RFC 5424 log format, the message header is built according to RFC 5424:
<PRI>VERSION TIMESTAMP HOSTNAME APP-NAME PROCID MSGID SD MESSAGEwhere:
PRI– priority value derived from thelocal7facility and the log level,VERSION– format version, always1,TIMESTAMP– time of the log entry in UTC, in the RFC 3339 format with microsecond precision,HOSTNAME– Fudo Enterprise host name,APP-NAME– application name, alwaysfudo,PROCID– process ID,MSGID– message identifier, always-,SD– structured data field, always empty (-),MESSAGE– the actual log message, preceded by the component or module name.
The message content is identical for both log formats. In the RFC 5424 format, Fudo Enterprise context data (object IDs and names) stays in the message content and is not moved to the structured data field.
For detailed list of log messages, refer to the Log Messages topic.
Editing Syslog Server Definition
To edit a Syslog server definition, proceed as follows.
Select > .
Open the Syslog Servers tab and click the name of the server you want to edit.
Modify the server definition as needed.
Click .
Deleting Syslog Server Definition
To delete a Syslog server definition, proceed as follows.
Select > .
Open the Syslog Servers tab.
Select the checkbox next to the server you want to remove.
Click and confirm the deletion.
Exporting Events Log
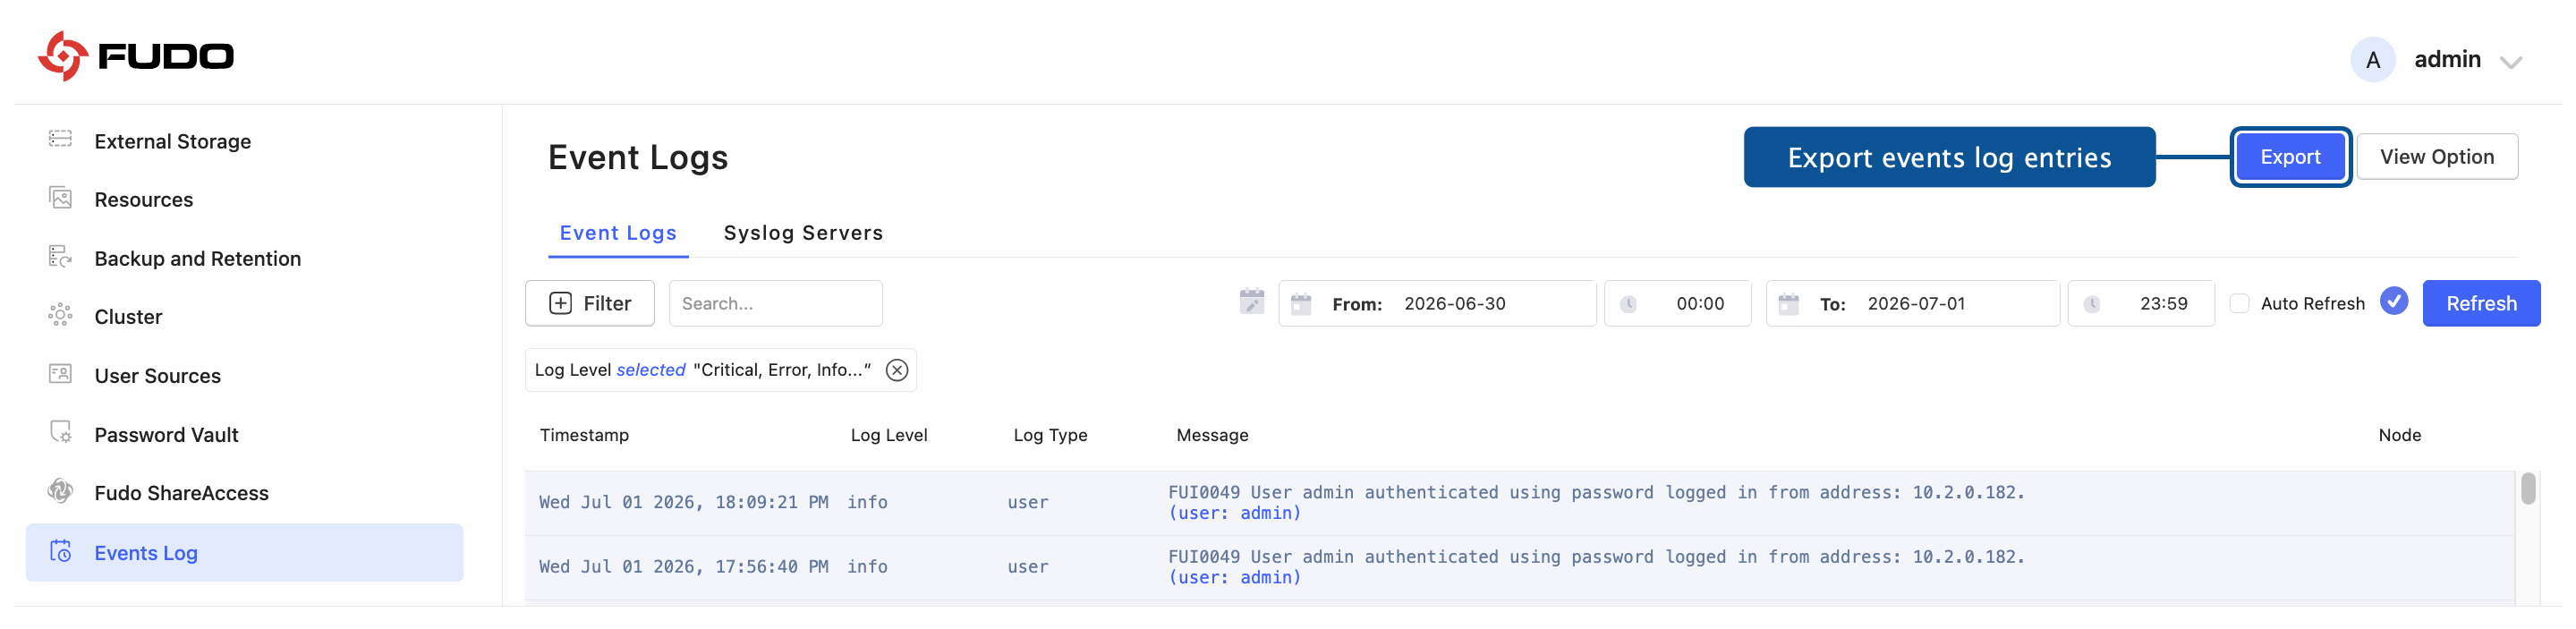
To export events log entries, proceed as follows.
Select > .
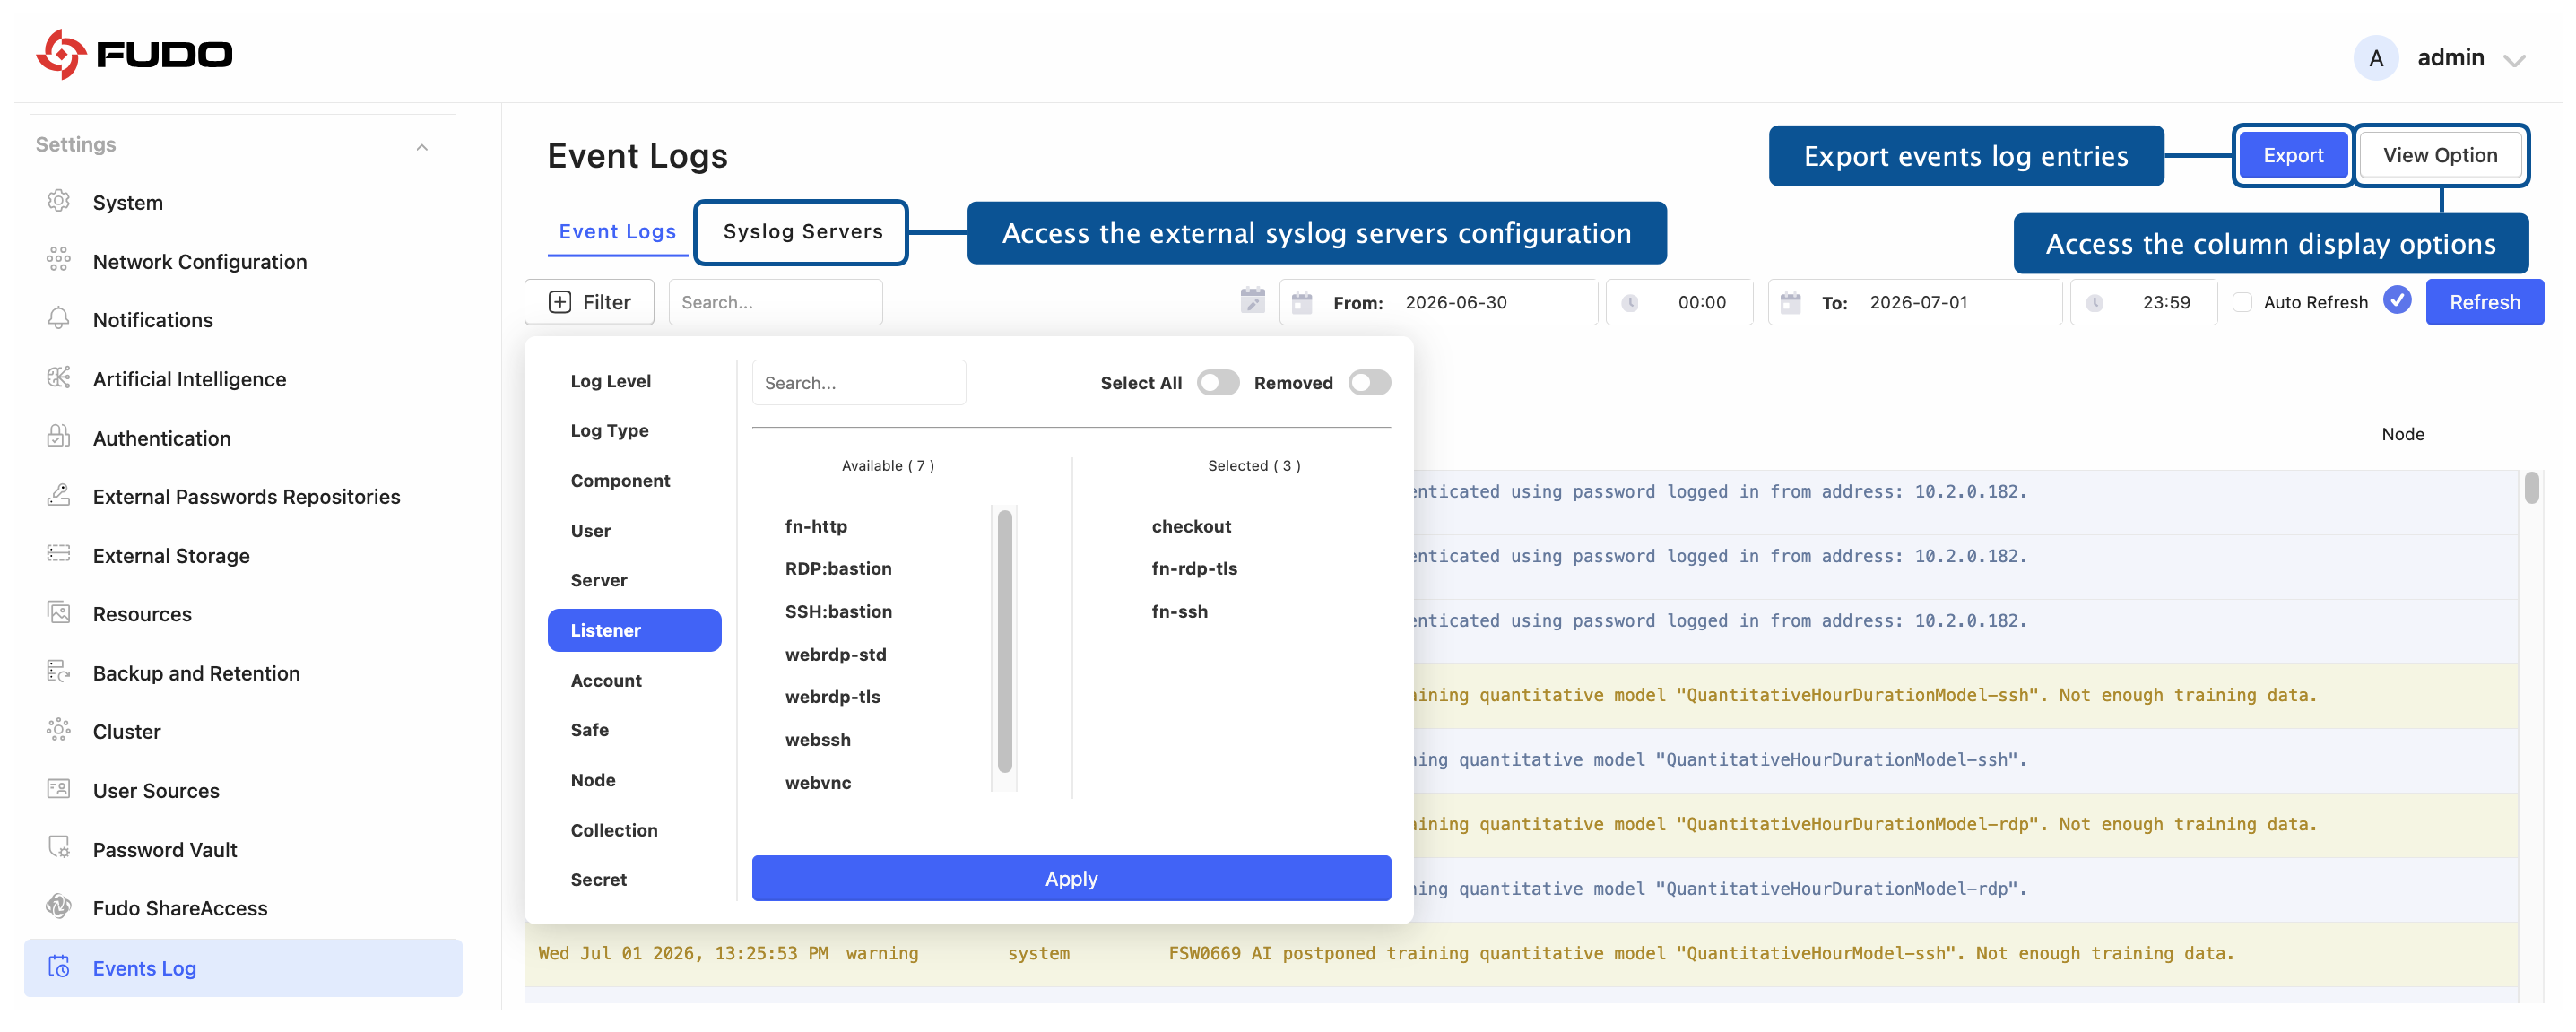
Click and select where to save exported log entries.
Related topics: