Location Policies
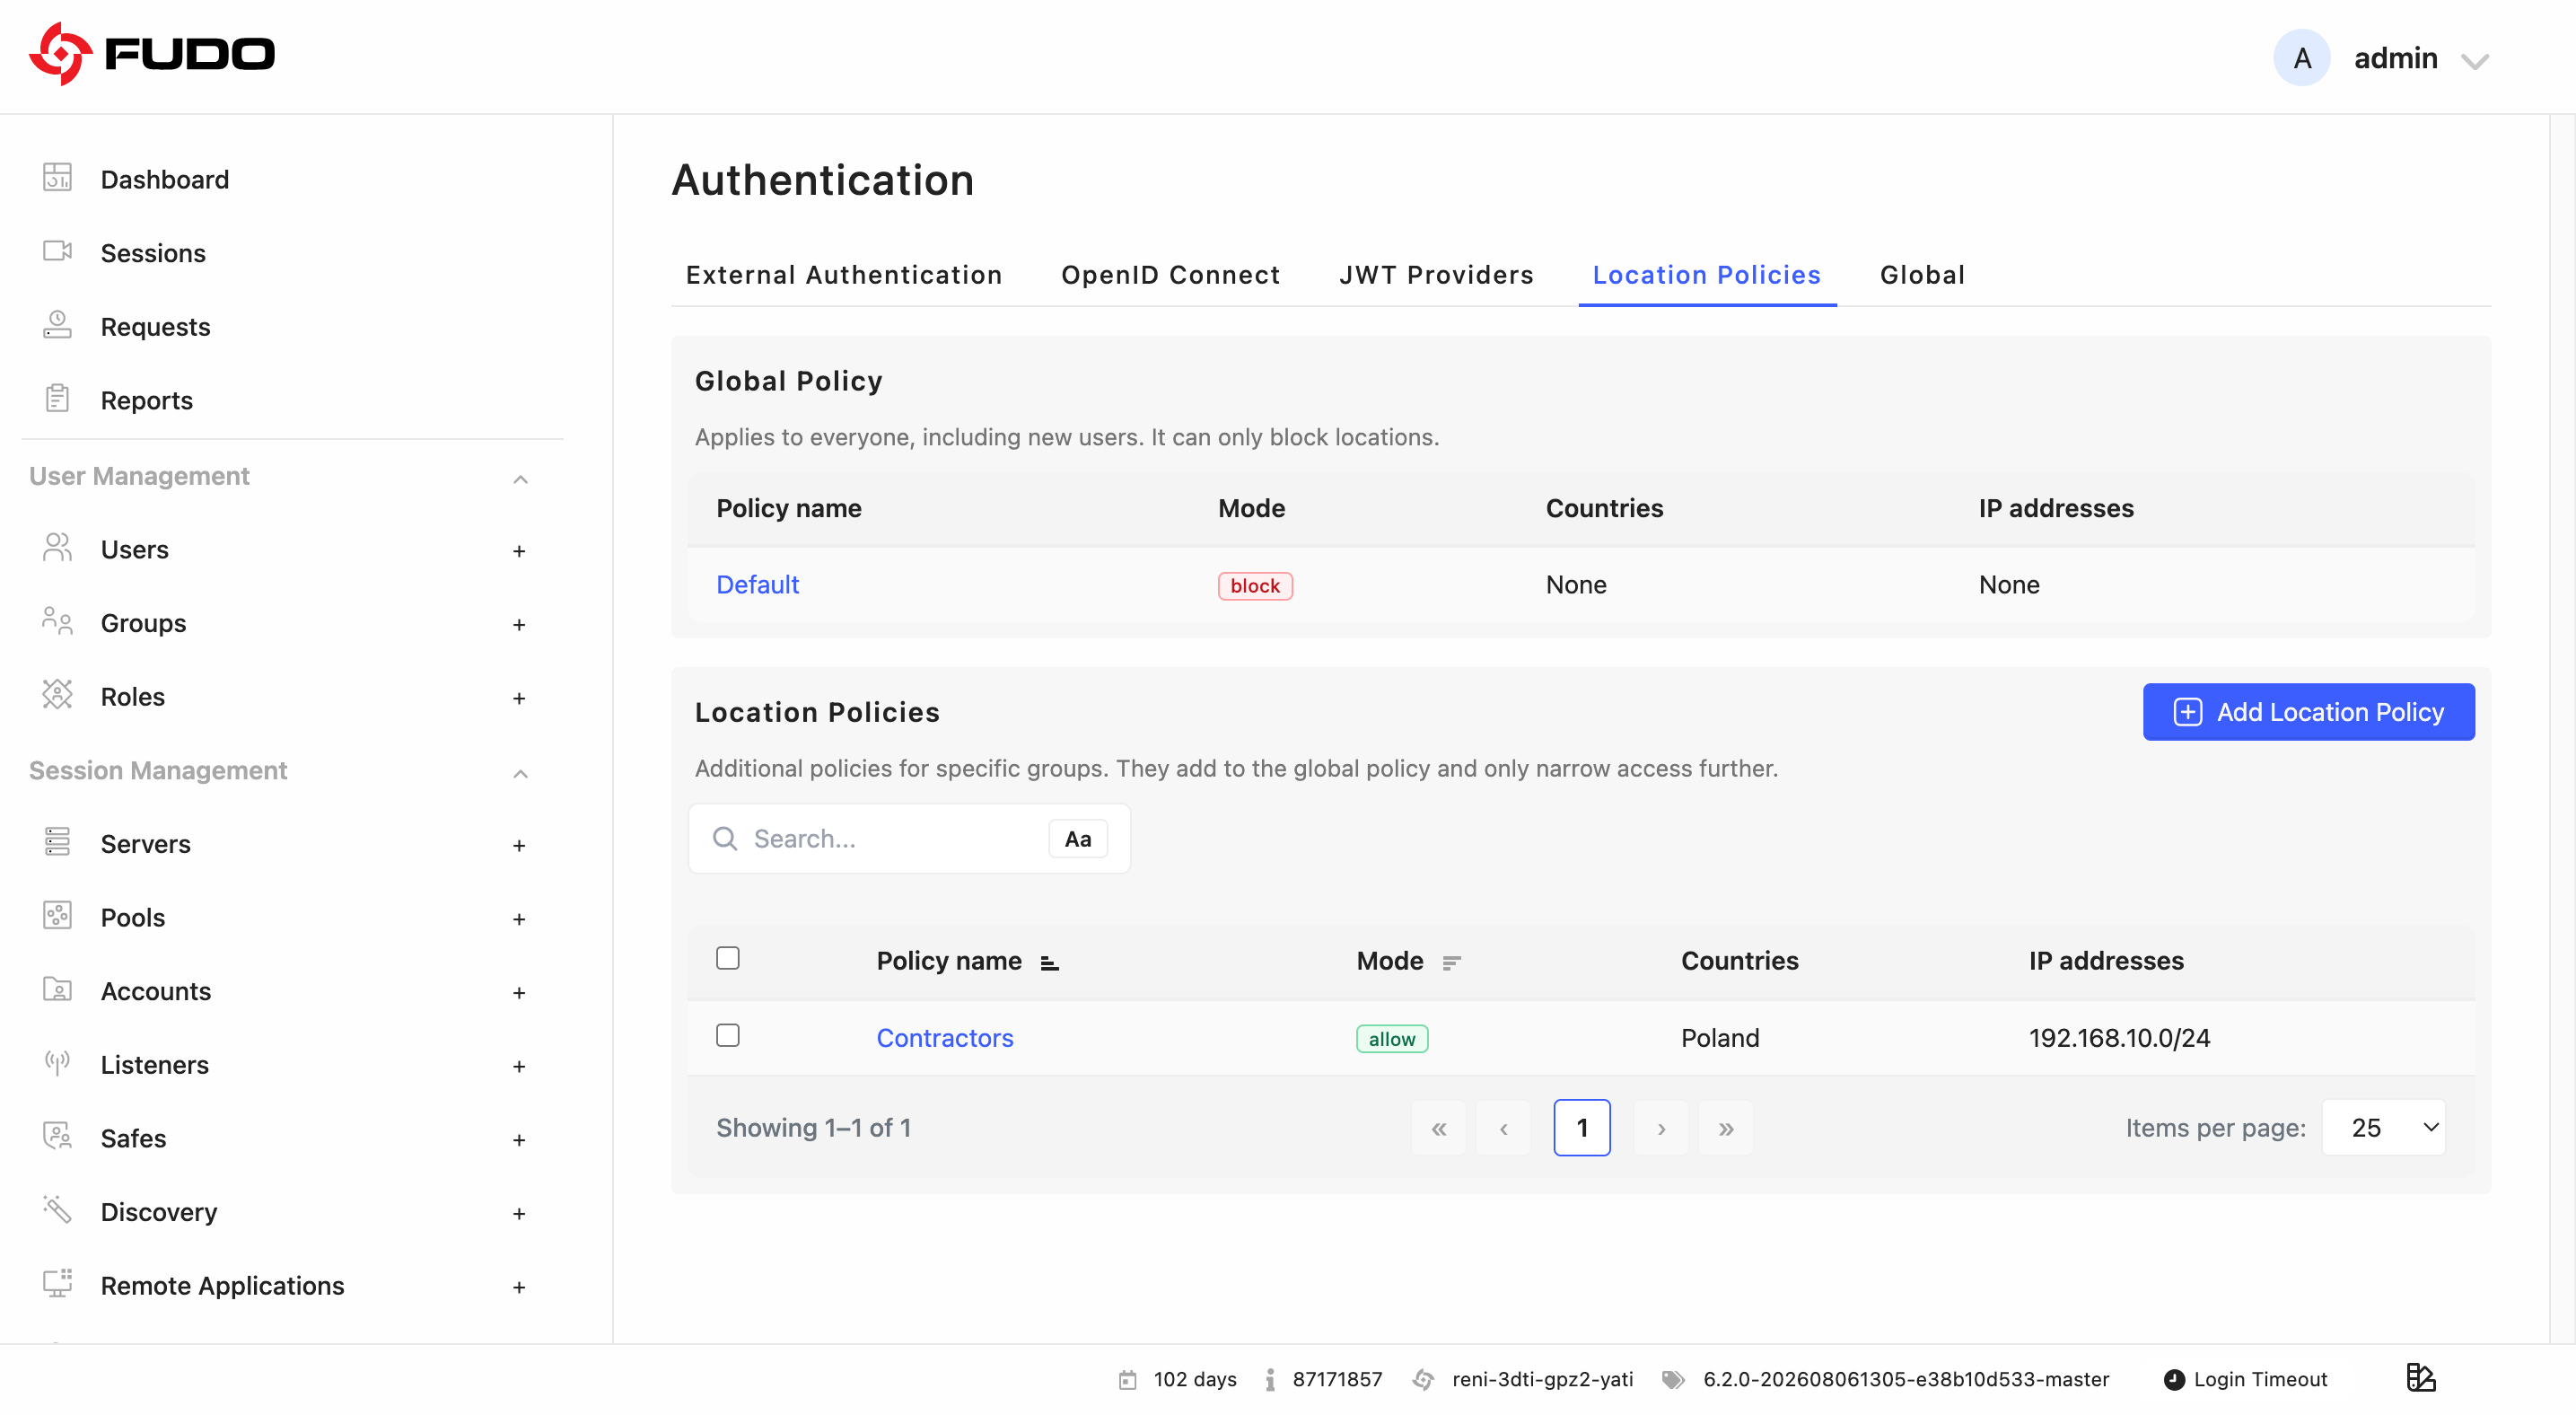
Location policies restrict where a user is allowed to authenticate from. A location is expressed as a country, recognised from the source IP address using the built-in GeoIP database, or as an IP address range given in CIDR notation.
Fudo Enterprise distinguishes two kinds of policies:
the global policy, which applies to every user and can only block locations,
additional policies, which are assigned to user groups and narrow access down further.
Note
Both kinds are empty after installation and after an upgrade, so no location is restricted until you add the first entry.
How Policies Are Combined
A user is never governed by a single policy. Their effective policy set consists of the global policy plus the policies of every group the user belongs to. Fudo Enterprise evaluates that whole set on each attempt, in the following order:
IP address entries are checked first.
Country entries are checked next.
Important
Blocking always wins. If any policy in the effective set blocks the location, access is denied - even when another policy explicitly allows it. An Allow connections policy therefore cannot re-open a location that the global policy or another group policy blocks.
This is also why the global policy has no Allow mode: it is the baseline that everyone shares, and it can only take access away.
Note
A policy with the Allow connections mode restricts the users of its groups to the locations listed in it. A policy with the Block connections mode leaves every other location available.
Configuring the Global Policy
The global policy is a built-in policy named Default. It cannot be renamed, deleted or assigned to a group - only its entries can be edited.
Select > .
Go to the Location Policies tab.
In the Global Policy section, click the Default policy.
Under Block connections from:, add the locations to be blocked for everyone:
click and select the countries,
click and provide the Address and Mask, optionally with a Description.
Click .
Adding a Location Policy for a Group
Select > .
Go to the Location Policies tab.
In the Location Policies section, click .
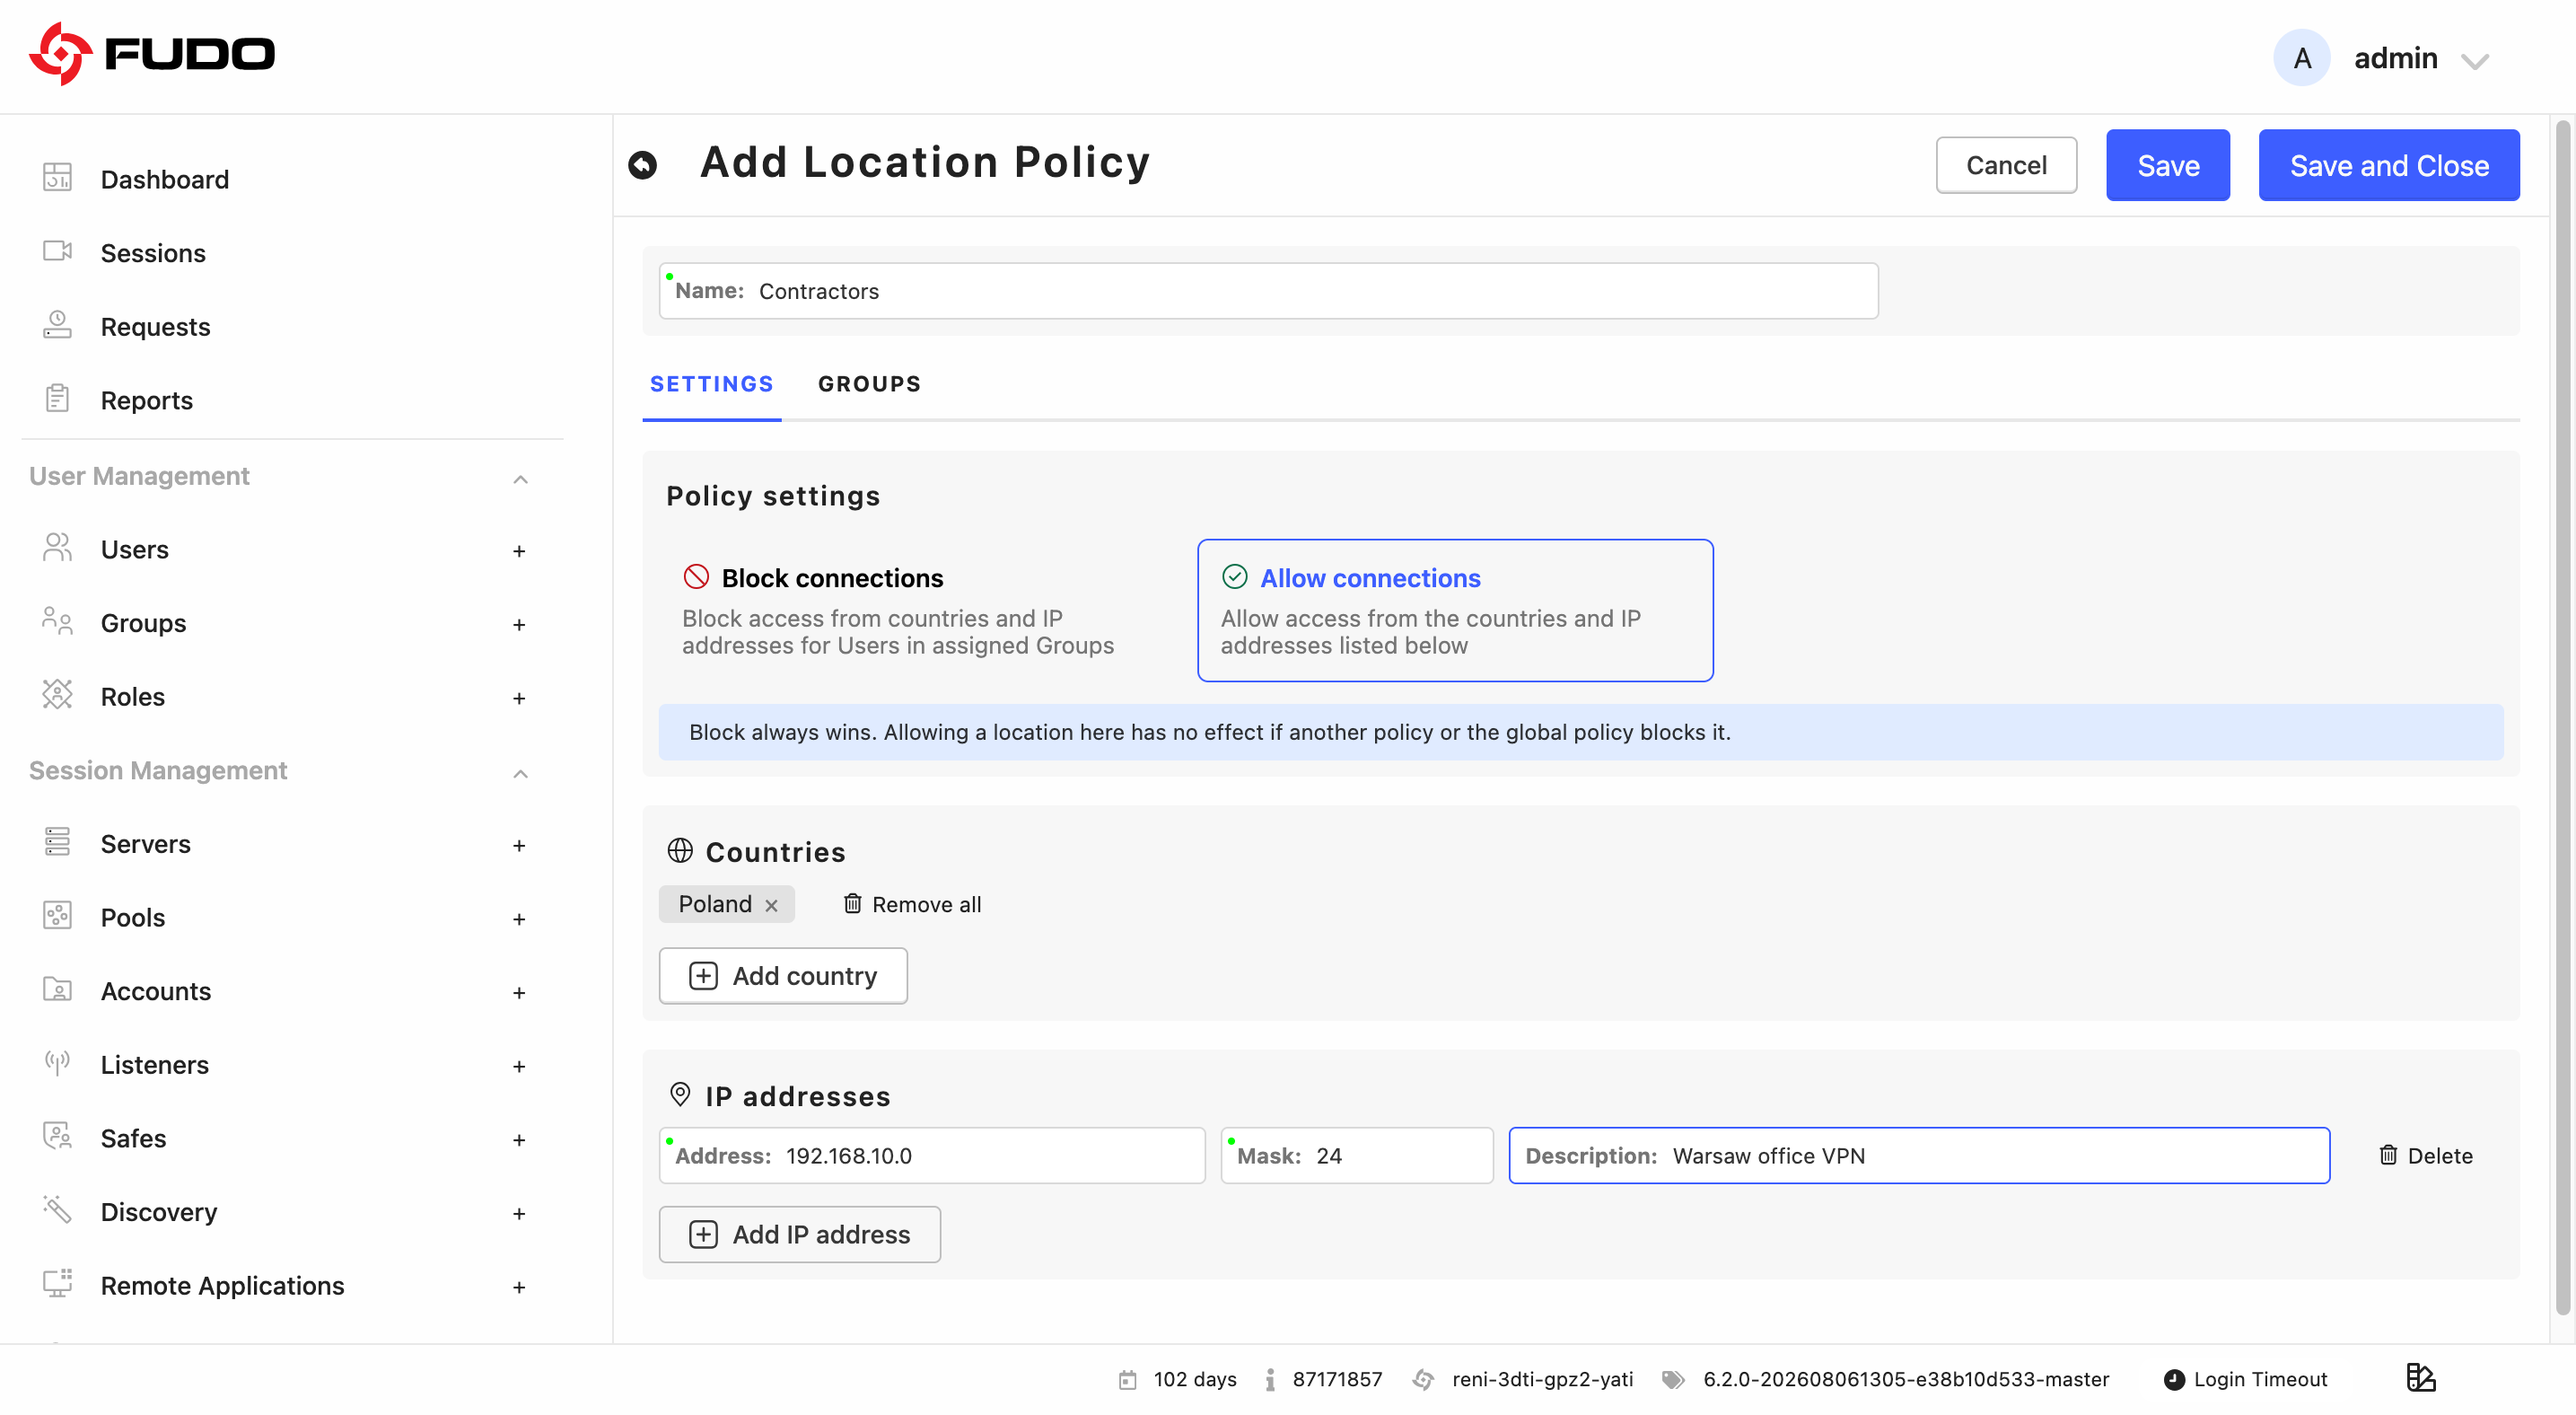
Enter the policy Name.
On the Settings tab, choose the mode:
Block connections - block access from the listed locations,
Allow connections - allow access only from the listed locations.
Add the locations in the Countries and IP addresses sections.
Click .
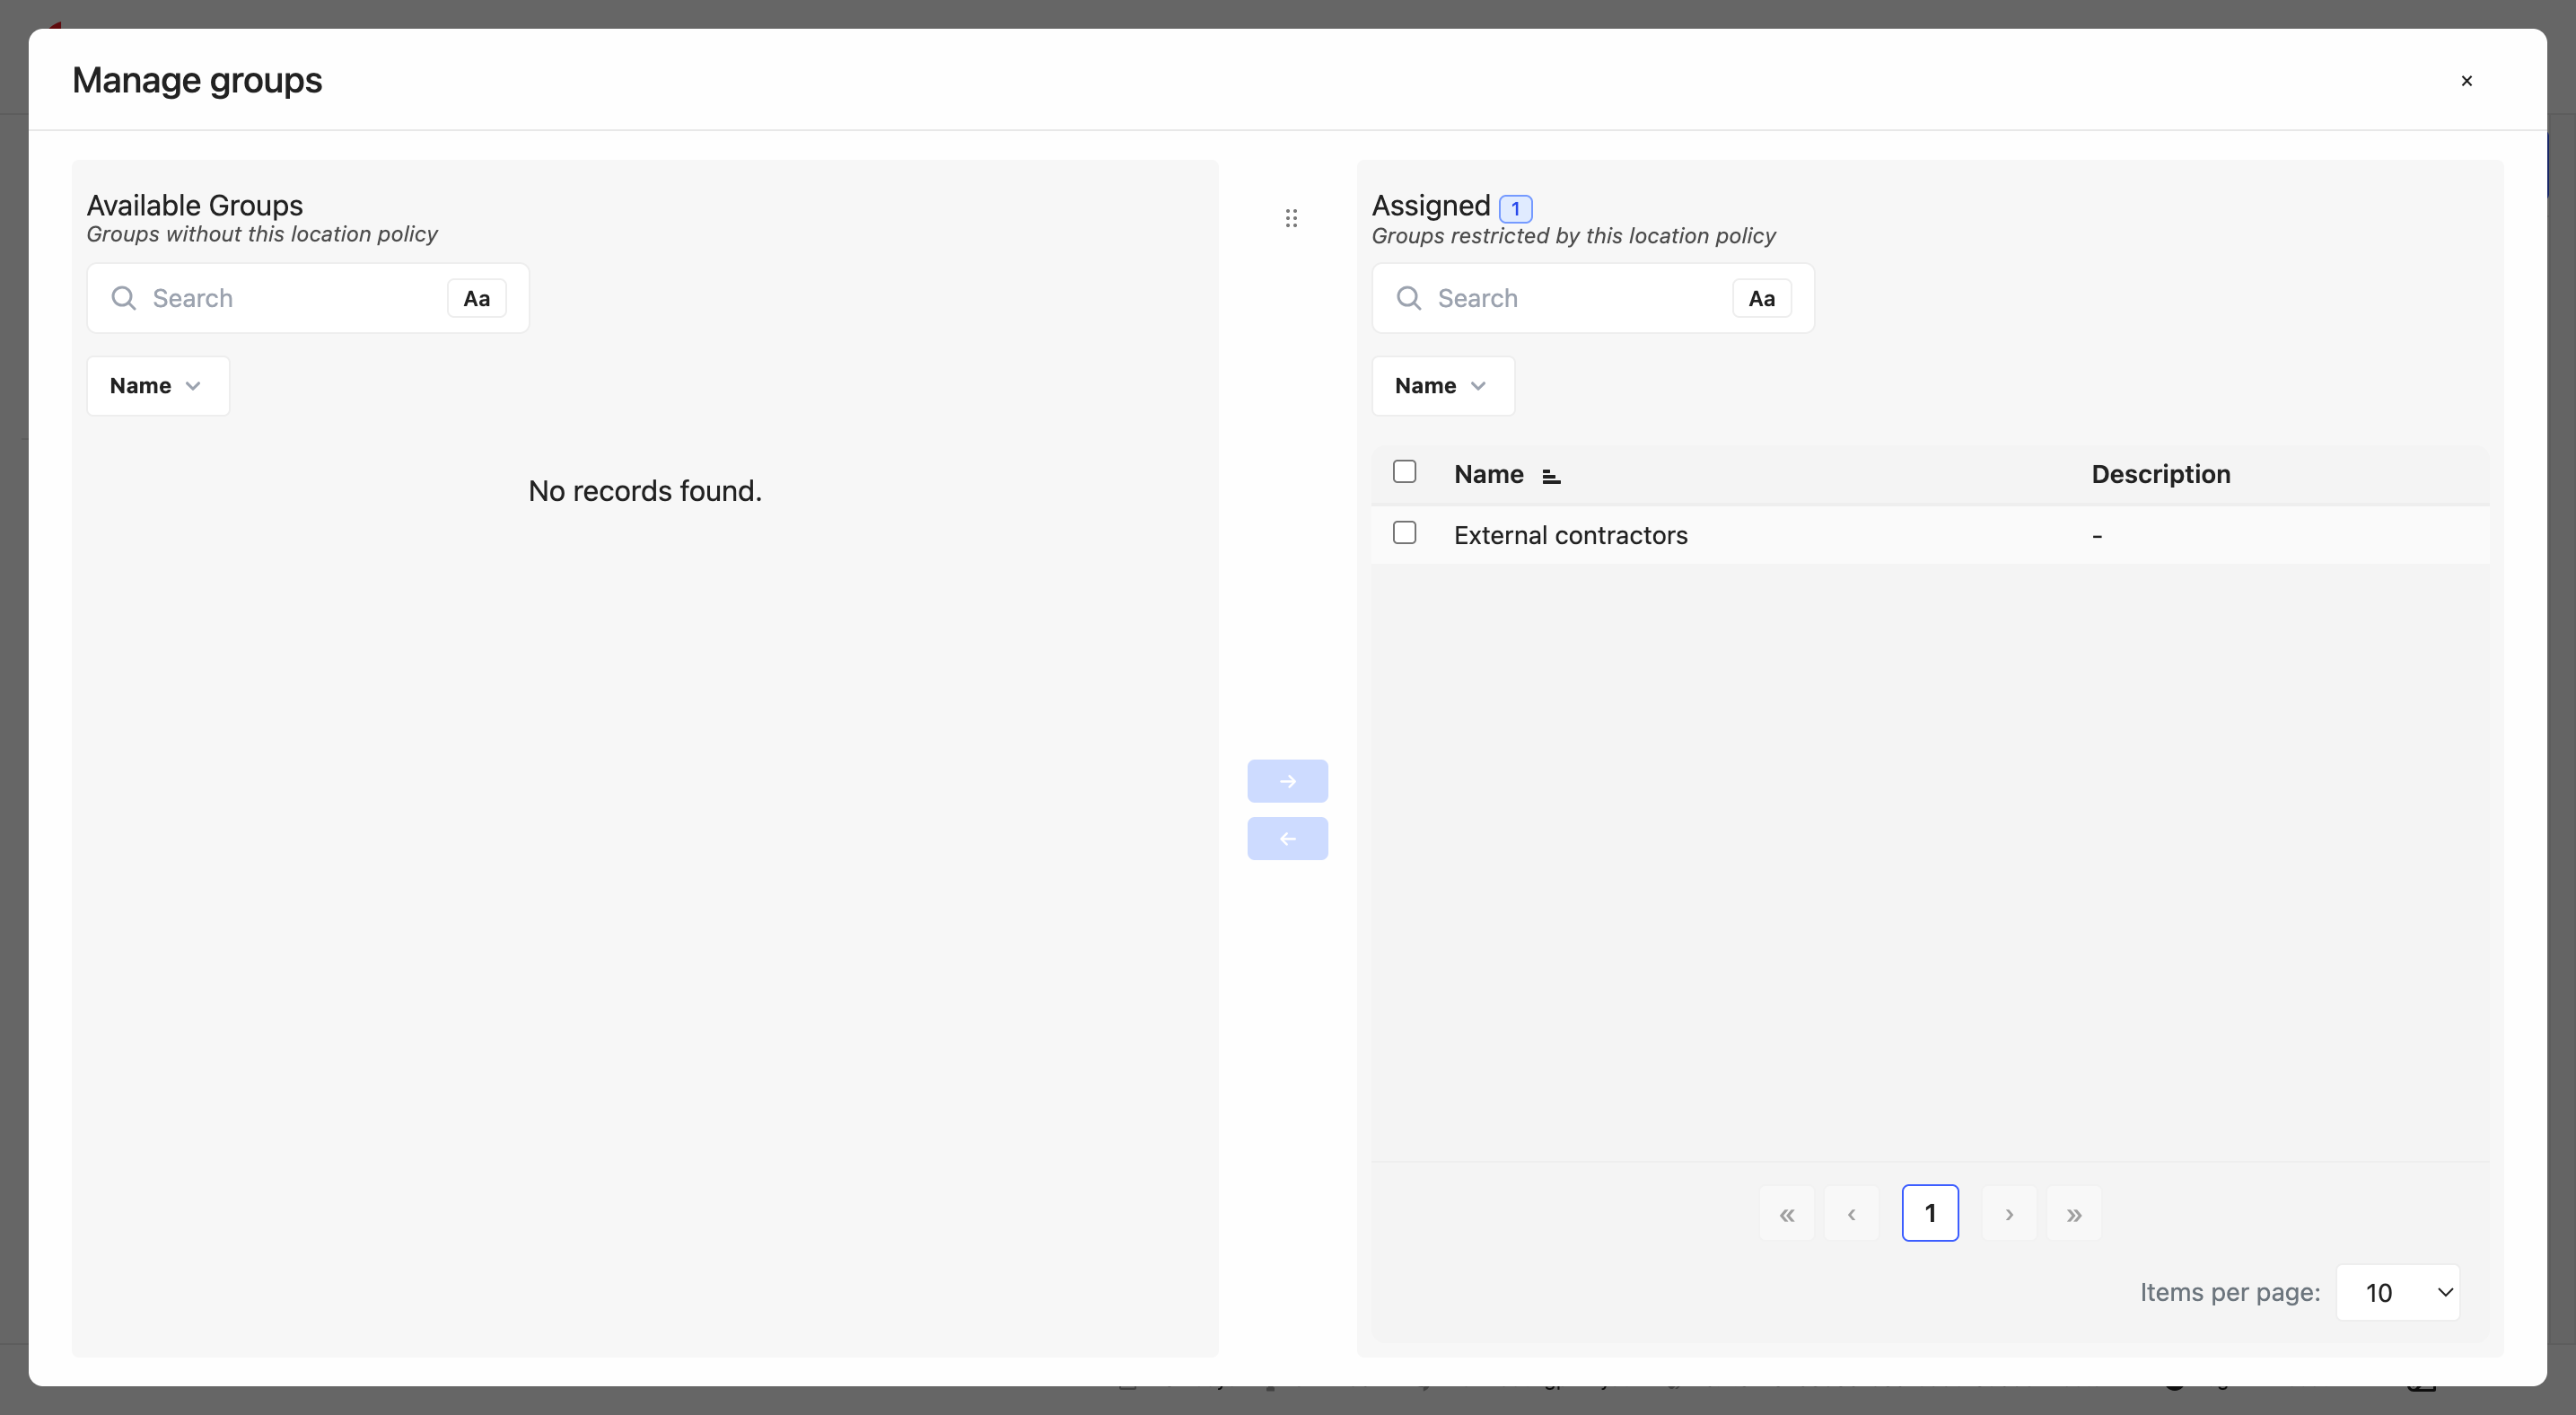
Go to the Groups tab, click , select the groups in Available Groups and move them to Assigned with the arrow button.
Note
A policy takes effect only once it is assigned to at least one group. When you create a policy, save it first - the Groups tab becomes available afterwards.
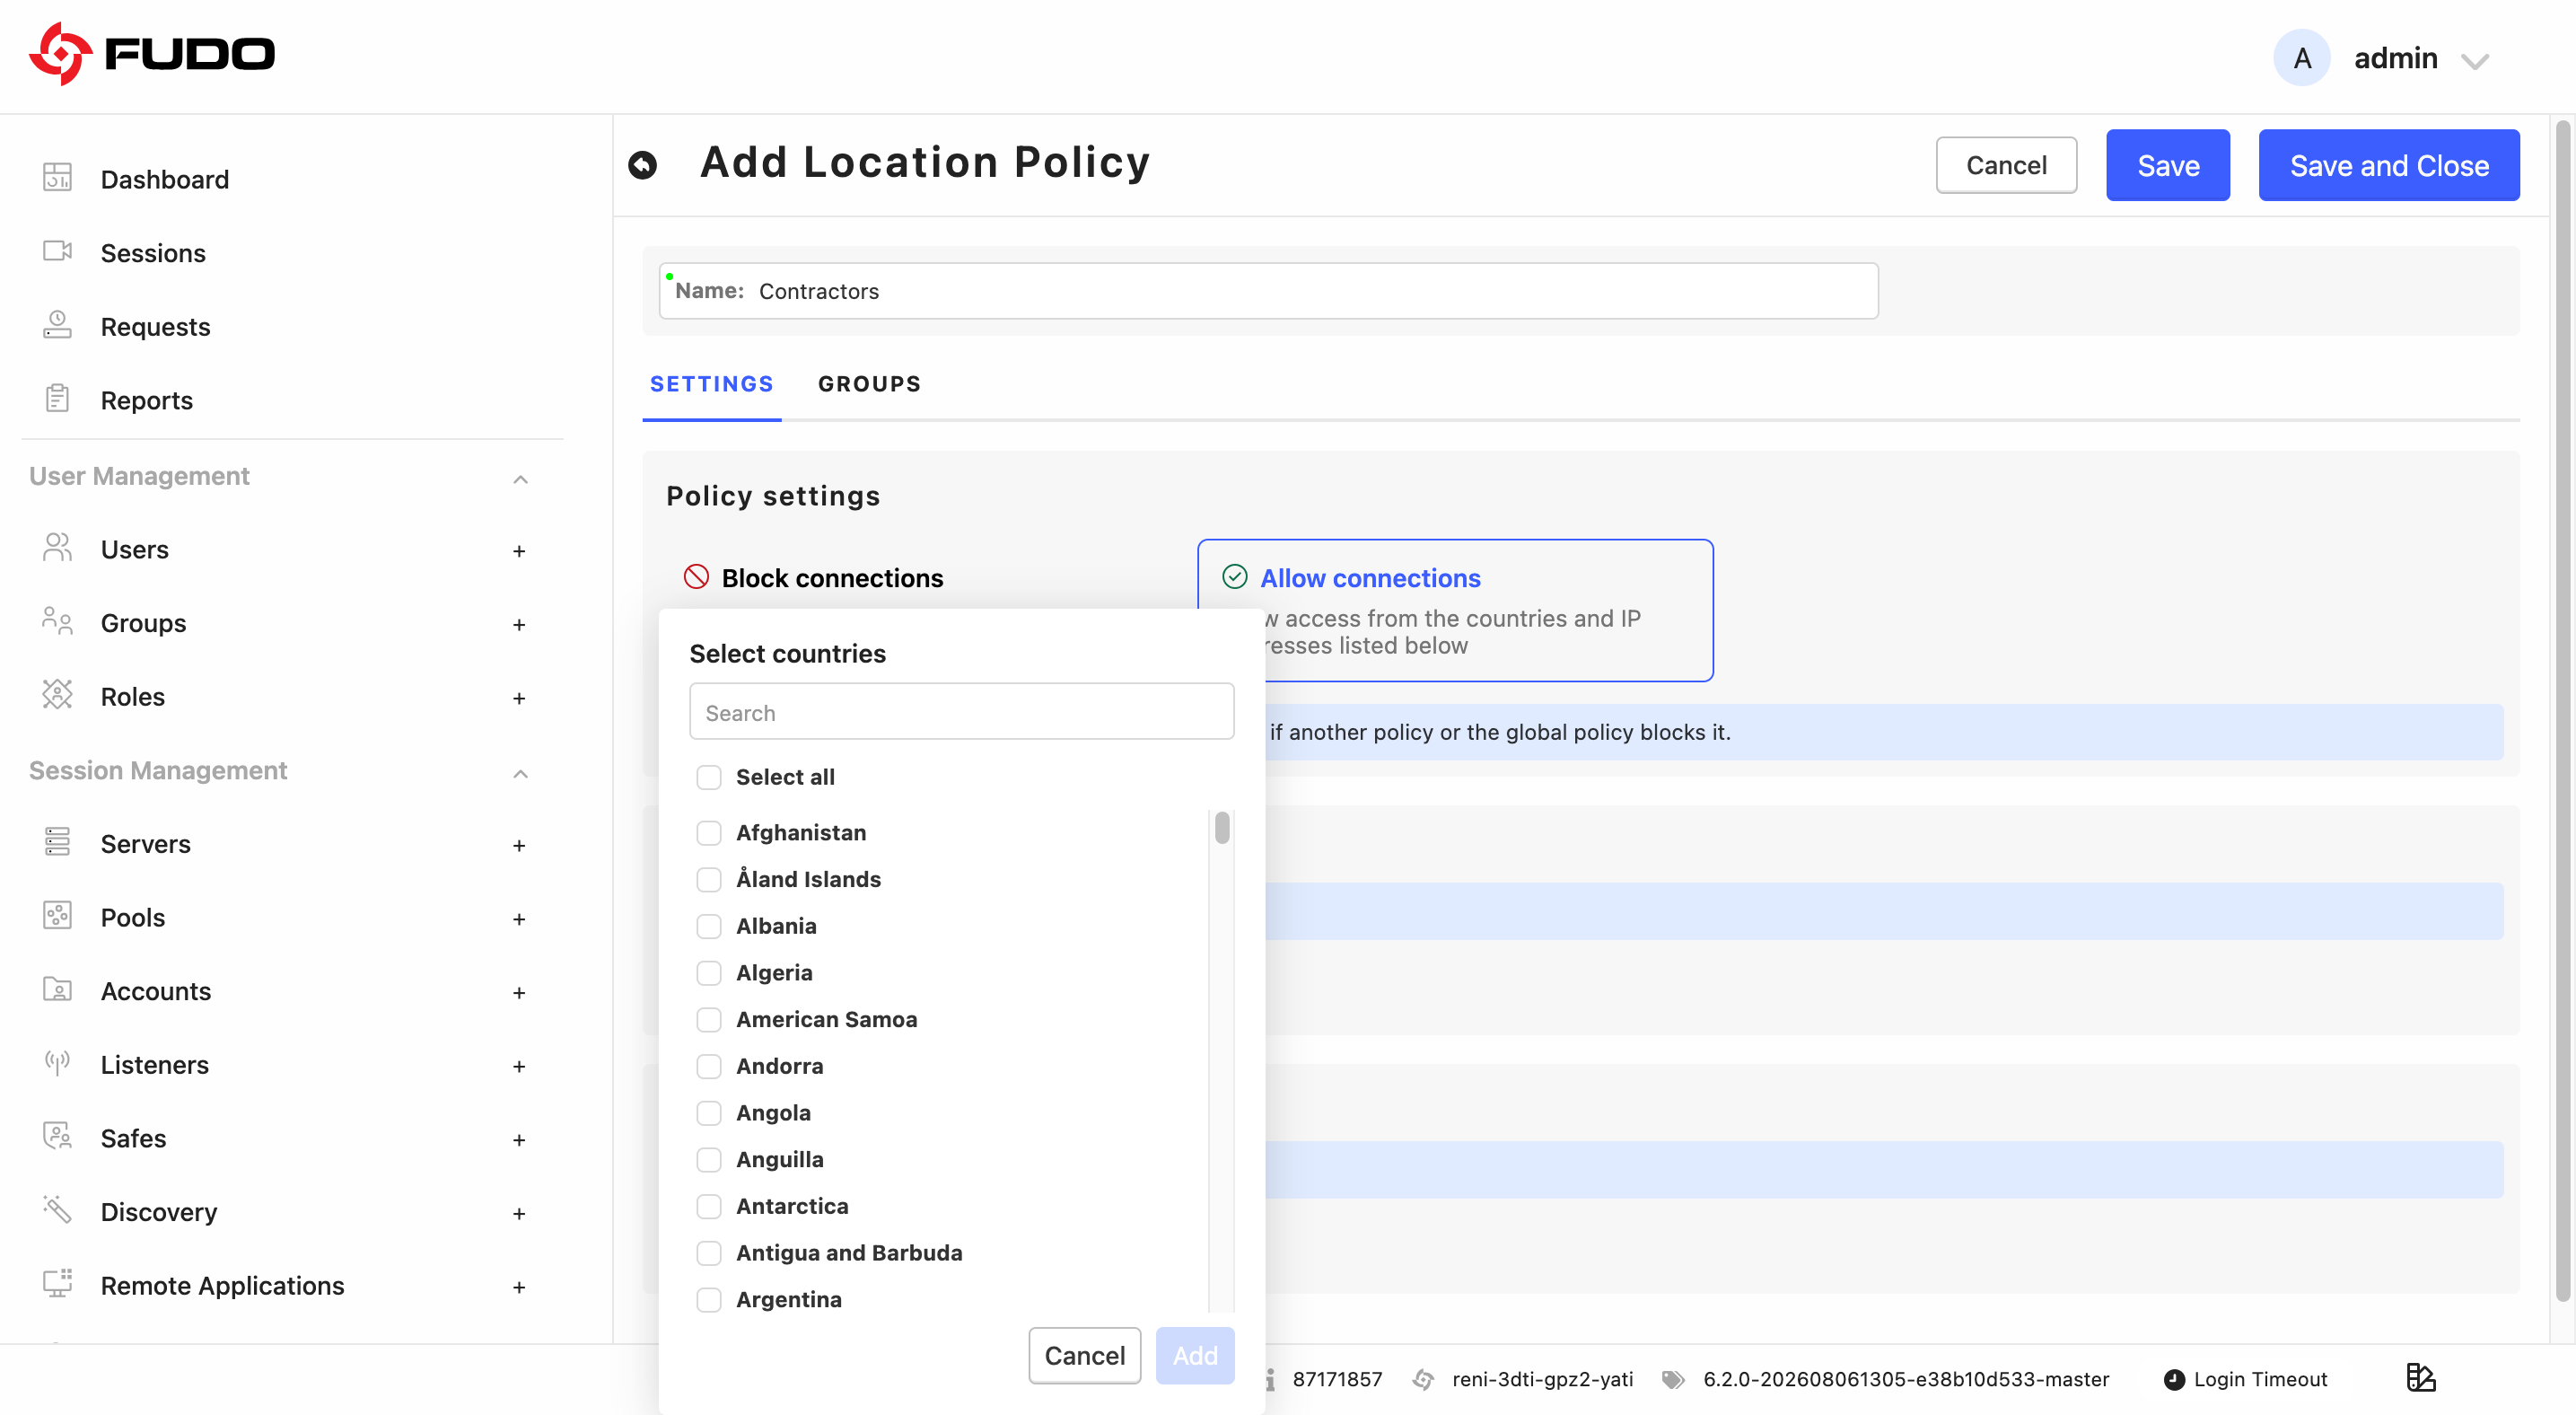
Selecting countries
The country list comes from the GeoIP database. Use the search field to narrow it down, or Select all to take every country at once, then confirm with Add. Selected countries are shown as removable chips.
Providing IP address ranges
An IP entry consists of the Address, the Mask given as a prefix length, and an optional Description. The address must be the network address of the range. If it contains host bits - for example 192.168.10.7/24 - Fudo Enterprise reports it and offers the correct network address (192.168.10.0/24) to apply with one click.
Where Policies Are Enforced
The effective policy set is evaluated at every authentication and on every API request:
when a user authenticates to establish a session, including the User Access Gateway web client, one-time password logins and tunnels,
on every request to the Fudo Enterprise API - so a session token acquired from an allowed location and then reused from a blocked one is rejected,
on SCIM requests used for user provisioning.
Important
Existing sessions are not affected. The location is verified when access is granted, not repeatedly during a session, so changing a policy does not terminate sessions that are already running. The same applies to taking a password out of the password vault.
Note
Requests that carry no source IP address - such as those from the Fudo Officer application - are not subject to location policies.
When the Location Cannot Be Determined
If the GeoIP database is unavailable or the source address cannot be resolved to a country, Fudo Enterprise grants access and records the event in the events log. This prevents a GeoIP problem from locking every user out.
Note
Private and link-local addresses have no country in the GeoIP database. Users connecting from the local network are therefore matched by IP address entries, not by country entries.
If the country list cannot be loaded while you are editing a policy, the Admin Panel displays a warning and falls back to country codes instead of names. IP address entries remain fully editable.
Protection Against Locking Yourself Out
Fudo Enterprise verifies every change against the location you are currently connecting from. If saving would deny you access - by adding or editing an entry, switching the mode, assigning a policy to a group, or adding yourself to a group covered by a policy - the change is discarded and an error is displayed.
Note
The check covers only your current location. A policy that leaves your present address allowed can still block you later, from another network - review the effective set before you change your workplace.
Required Privileges
Location policies use the same privileges as the rest of the authentication configuration: authentication-read to view them and authentication-modify to change them. Refer to Role-Based Access Control (RBAC) for details on assigning privileges to roles.
Related topics: