External Authentication Server Definition
To add an external Active Directory, LDAP, Cerb, RADIUS, or TACACS+ authentication server, proceed as follows.
Select > .
Choose External authentication tab.
Click .
Provide a name for this specific configuration.
Select the bind address - IP address used for sending requests to given host.
Note
In case of cluster configuration, select a labeled IP address from the Bind address drop-down list and make sure that other nodes have IP addresses assigned to this label. For more information refer to the Labeled IP Addresses topic.
In the General section, select authentication service type:
Active Directory, LDAP, CERB, RADIUS,orTACACS+.

Provide configuration parameters depending on selected external authentication system type. Configuration details are described in the sections below.
Click .
Field Descriptions and Configuration Based on Chosen Method
Active Directory
Parameter |
Description |
|---|---|
Active Directory domain |
Domain which will be used for authenticating users in Active Directory. |
TLS enabled |
This option is required to be checked for the domain users who change their passwords in the User Access Gateway. |
CA Certificate |
Available when TLS enabled option is activated. |
Privileged user login |
The privileged account’s login name to modify a user password on the Active Directory server. The field is located in the Credentials subsection. |
Secret |
Secret used to establish server connection to modify a user password on the Active Directory server. The field is located in the Credentials subsection. |
Add second factor |
Additional verification step with authentication methods |
Note
The Active Directory external authentication method uses the Kerberos protocol as the first step.
This functionality is enabled by default.
Please refer to Kerberos Authentication Settings section to learn how to disable it.
If Active Directory authentication is successfully completed using Kerberos, the configured certificate will not be applied, as it is only utilized when a fallback to LDAP is required.
To enforce Kerberos-only authentication, you can disable the fallback to LDAP simple bind authentication on the Kerberos Authentication Settings page (the Disable LDAP fallback option). If Kerberos is then unavailable, Active Directory authentication fails.

LDAP
Parameter |
Description |
|---|---|
Host |
Server’s host name or IP address. |
Port |
Port used to establish connections with given server. |
Bind DN |
Template containing a path which will be used to create queries to LDAP server (for example: |
TLS enabled |
This option is required to be checked for the domain users who change their passwords in the User Access Gateway. |
Server certificate / CA Certificate |
LDAP server certificate or CA certificate. Available when TLS enabled option is activated. |
Add second factor |
Additional verification step with authentication methods |

Note
The value of Bind DN field may include variable substitution, allowing the DN to be dynamically generated based on the username of the user logging in to the system, for example: cn=##username##,dc=example,dc=com
In that case, when configuring a user, leave the LDAP Base field empty in > > User Data tab.
The following description assumes that user’s authentication data is stored on LDAP server accessible through 10.0.0.2 IP address and default LDAP service port number - 389. User definition is stored under dc=example,dc=com.

Cerb
Parameter |
Description |
|---|---|
Host |
Server’s IP address. |
Port |
Port used to establish connections with given server. |
Service (NAS ID) |
CERB service used for authenticating Fudo Enterprise users. |
Secret |
Secret used to establish server connection. |
Add second factor |
Additional verification step with authentication methods |

Note
The AD domain field from the user configuration is included in the initial Access-Request packet used to authenticate the user against the RADIUS/Cerb server.
If the AD domain is populated:
For RADIUS, the AD domain value is appended to the username in the
User-Namefield, formatted as:{name}@{ad_domain}. This behavior is controlled by the Append domain to username option described in the Radius section. When the option is disabled, theUser-Namefield contains only{name}, even if the AD domain is populated.For Cerb, the
MS-CHAP-Domainfield is set to the value from the AD domain, and theUser-Namefield contains only{name}. The Append domain to username option does not apply to Cerb.If the AD domain is not populated, the
User-Namefield in theAccess-Requestpacket for both methods contains only the username:{name}.
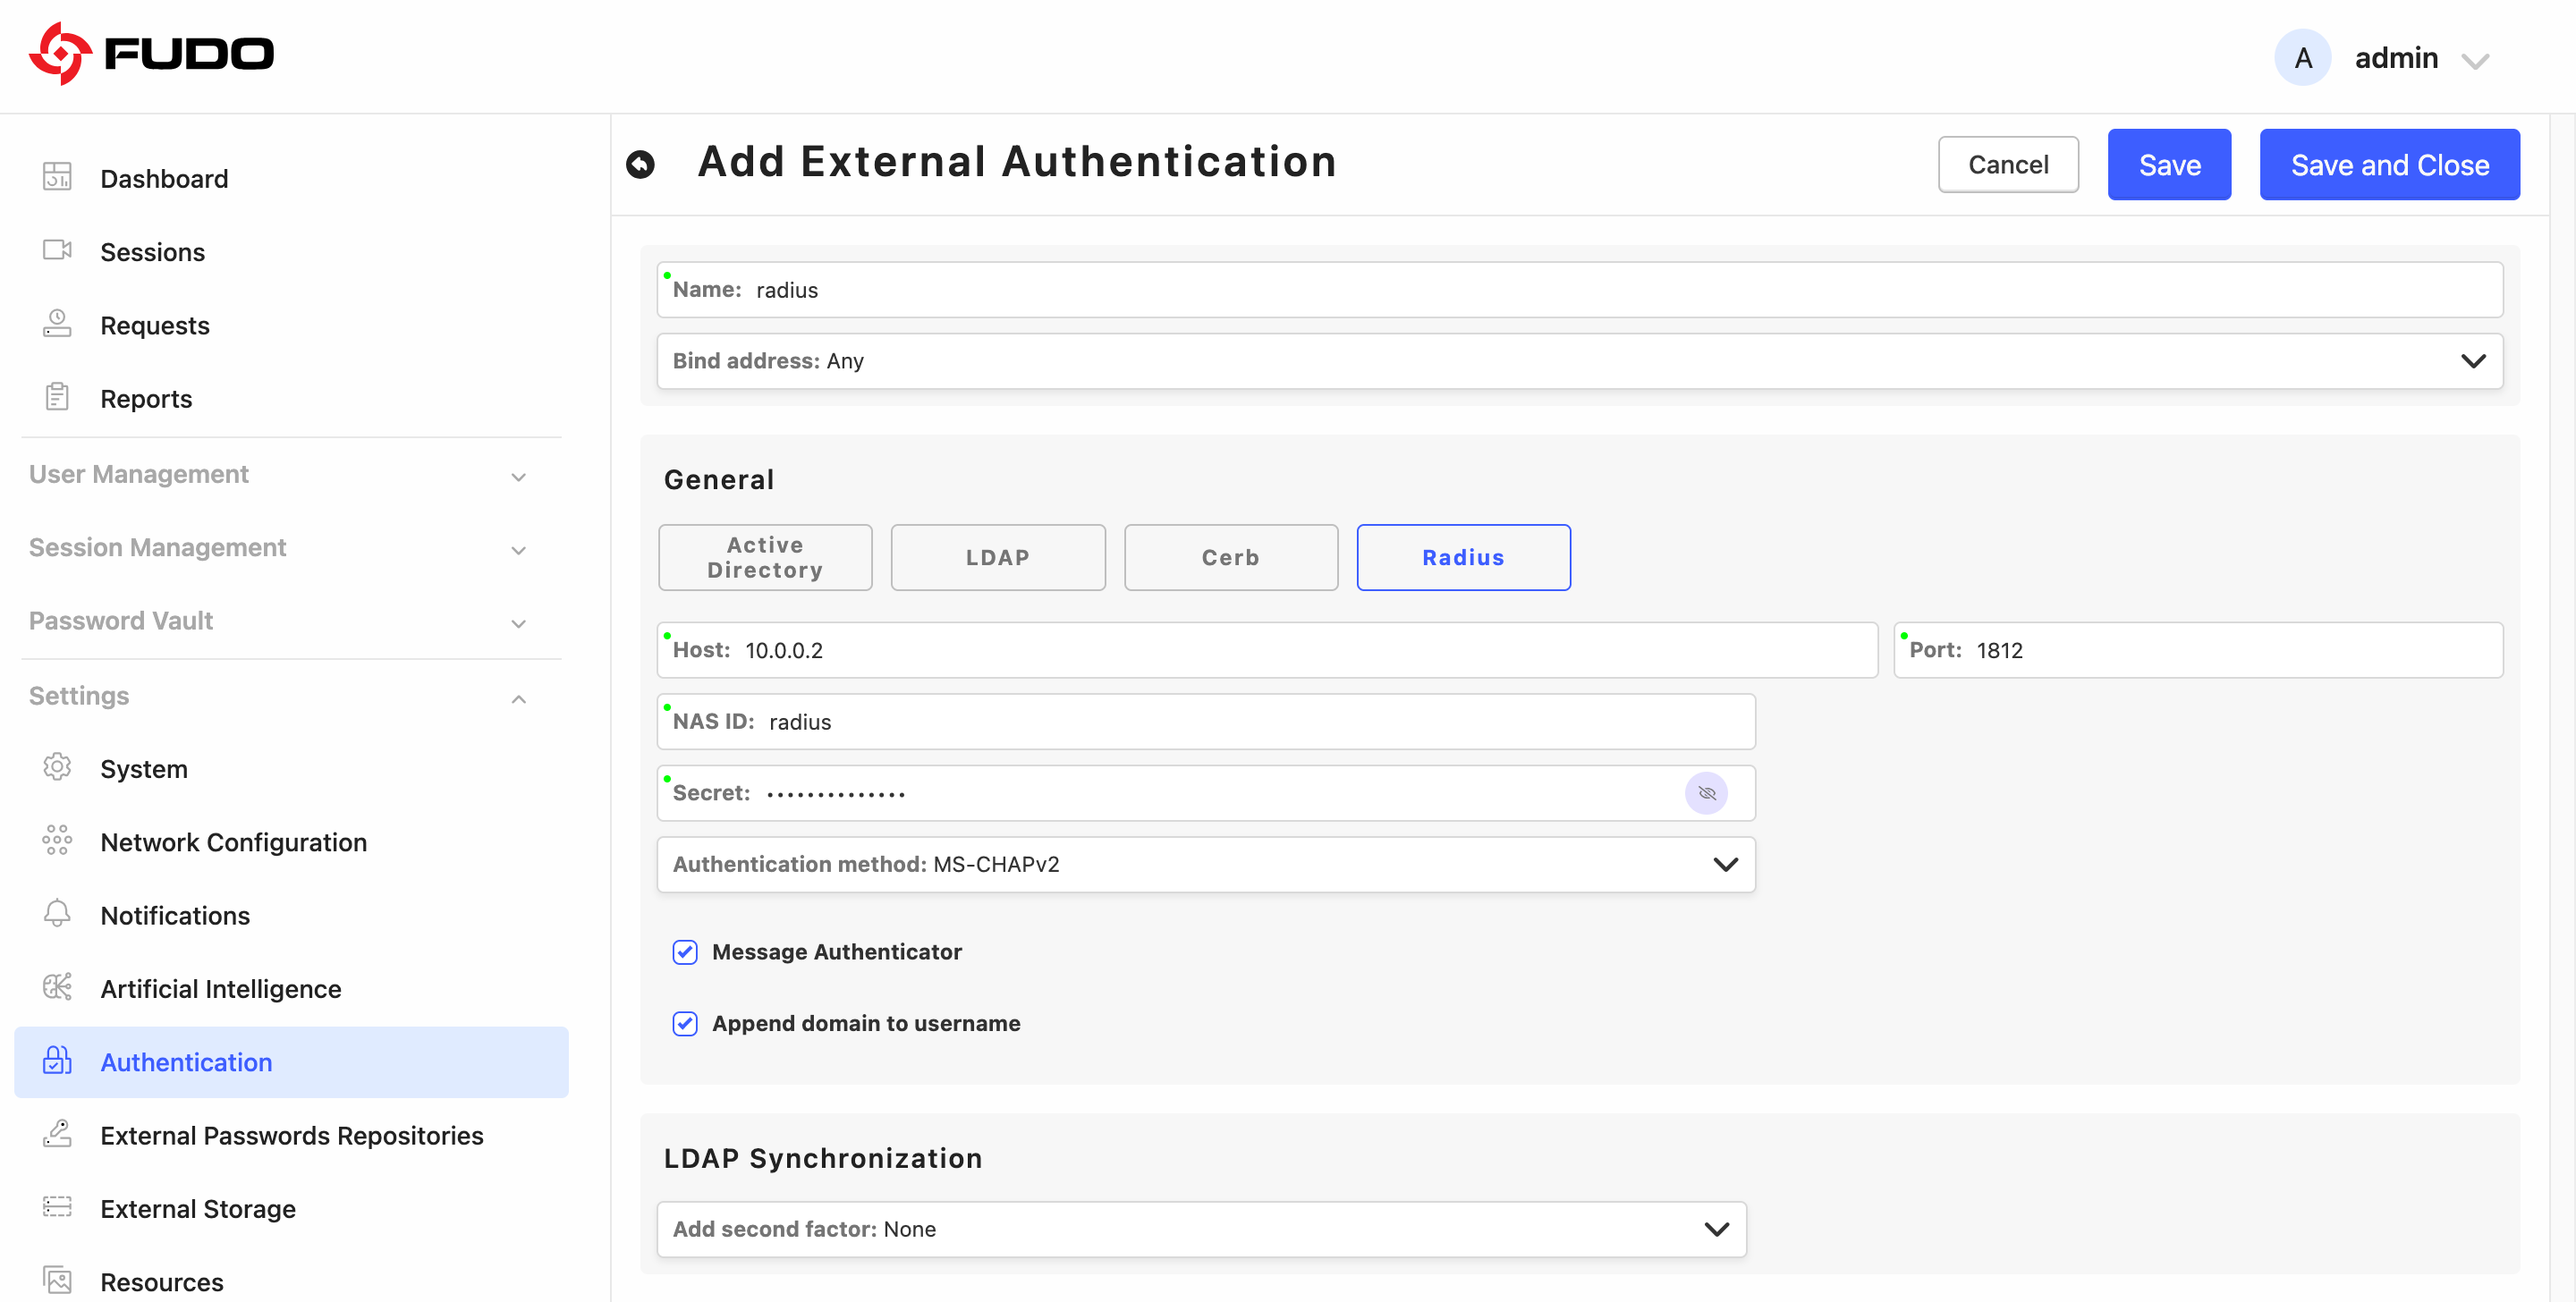
Radius
Parameter |
Description |
|---|---|
Host |
Server’s IP address. |
Port |
Port used to establish connections with given server. |
NAS ID |
RADIUS server NAS-Identifier parameter. |
Secret |
Secret used to establish server connection. |
Authentication method |
Select authentication method PAP, CHAP, MS-CHAPv2 |
Message Authenticator |
Adds the |
Append domain to username |
Decides whether the user’s AD domain is appended to the login sent to the RADIUS server. When the option is selected (default), the |
Add second factor |
Additional verification step with authentication methods |
Note
The CHAP authentication method does not work in Windows environments.
The Append domain to username option is selected by default, also for the external authentication server definitions that already existed before the upgrade. The way the username is sent to the RADIUS server does not change until you clear the option.
Make sure to read the note for the Cerb method as well.
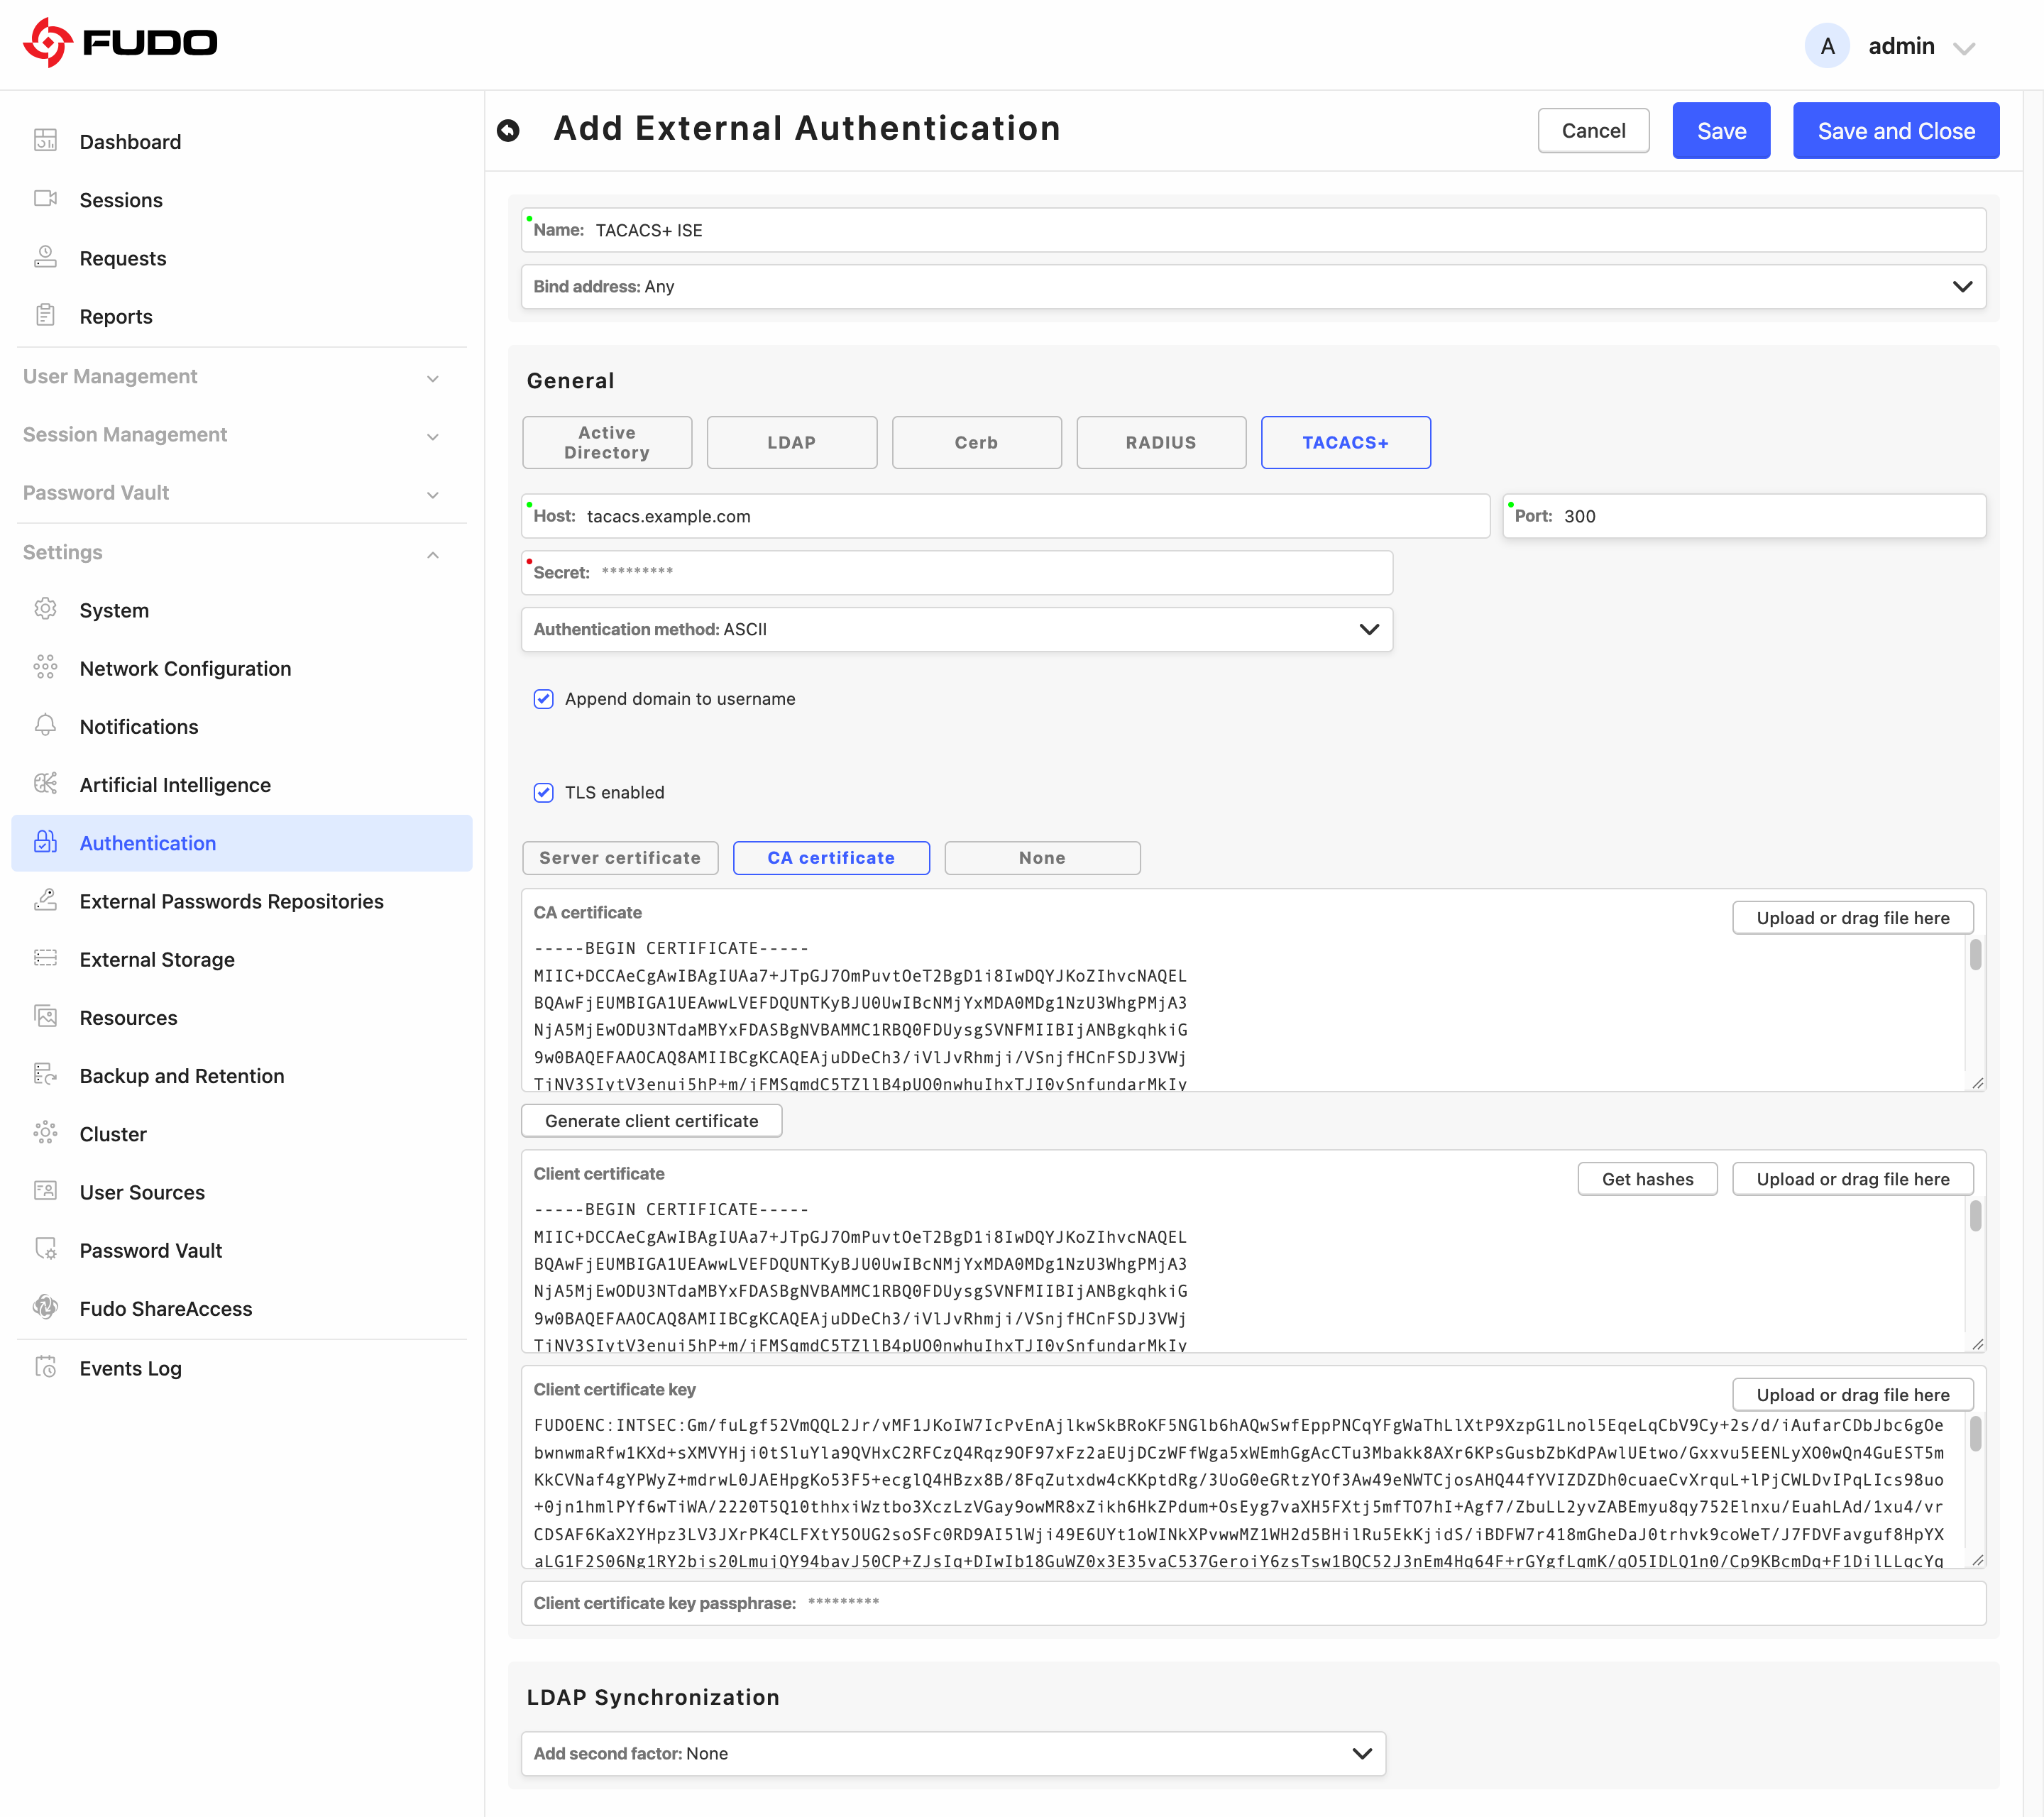
TACACS+
Parameter |
Description |
|---|---|
Host |
Server’s host name or IP address. |
Port |
Port used to establish connections with the TACACS+ server. Default: |
Secret |
Shared key defined for Fudo Enterprise on the TACACS+ server. Required when TLS enabled is not selected. Over TLS, the key is not used and can be left empty. |
Authentication method |
Select ASCII (default), PAP, or CHAP. |
Append domain to username |
Decides whether the user’s AD domain is appended to the username sent to the TACACS+ server, in the |
TLS enabled |
Connects to the TACACS+ server over TLS 1.3 (RFC 9887). If the TLS connection fails, Fudo Enterprise does not fall back to an unencrypted connection. |
Server certificate / CA certificate / None |
Decides how Fudo Enterprise verifies the TACACS+ server: Server certificate accepts only the provided certificate, CA certificate accepts a certificate issued by the provided CA for the address given in Host, None does not verify the server. Use None for testing only. Available when TLS enabled is selected. |
Generate client certificate |
Generates a self-signed client certificate and its key. Use it when the TACACS+ server trusts this certificate directly. If the server verifies client certificates against a CA, upload a certificate issued by that CA instead. Available when TLS enabled is selected. |
Client certificate |
Certificate that Fudo Enterprise presents to the TACACS+ server. TACACS+ servers usually require it for TLS connections. If the certificate was issued by an intermediate CA, put the client certificate first, followed by the intermediate CA certificates. Available when TLS enabled is selected. |
Client certificate key |
Private key of the client certificate. It must match the client certificate. Available when TLS enabled is selected. |
Client certificate key passphrase |
Passphrase of an encrypted client certificate key. It is used only to decrypt the key and is not stored. Available when TLS enabled is selected. |
Add second factor |
Additional verification step with authentication methods |
Note
Fudo Enterprise uses TACACS+ for user authentication only. TACACS+ authorization and accounting are not used.
Without TLS, TACACS+ hides the content of the packets but does not protect it against modification. Select TLS enabled, or make sure that the connection to the TACACS+ server goes through a trusted network.
Additional prompts from the TACACS+ server, for example for a token, are supported only with the ASCII authentication method. In sessions to servers, they are supported for the SSH, RDP, and VNC protocols.
Assigning an External Authentication Method to a User
Select > .
Find and click the user definition for which you want to assign an external authentication method (e.g.
admin).Go to the User Data tab, in the LDAP Base field specify the location of this user object in the directory structure (e.g.
cn=admin,dc=example,dc=com).
Note
Leave the LDAP Base field empty if you specified where users are stored in the LDAP server configuration (cn=##username##,dc=example,dc=com).
To add authentication method, go back to the Settings tab and select External authentication from the Add authentication method drop-down list.
Choose method and click .
Click to save user definition.
Second Authentication Factor
If an additional verification step (the Add second factor option) is configured in the external authentication server definition using the OATH, SMS, or DUO authentication methods, the method selected as the second factor must be chosen as the authentication method in the user configuration. Then, in its configuration window, External Authentication must be selected as the first authentication factor.
Select > .
Find and click the user definition for which you want to assign an external authentication method (e.g.
admin).Go to the User Data tab, in the LDAP Base field specify the location of this user object in the directory structure (e.g.
cn=admin,dc=example,dc=com).
Note
Leave the LDAP Base field empty if you specified where users are stored in the LDAP server configuration (cn=##username##,dc=example,dc=com).
To add external authentication method with second factor, go back to the Settings tab and select the name of the method used in the configuration (e.g. SMS) from the Add authentication method drop-down list.
In the modal window, select External Authentication as the first authentication factor.
From the Choose method list, select the external authentication method configured with a second authentication factor, according to the scenario described above.
Configure parameters of the second factor.

Click .
Click to save user definition.

Related topics: